
AWS 060: Create the VPC, subnets, route tables, internet gateway, security group, and NACL
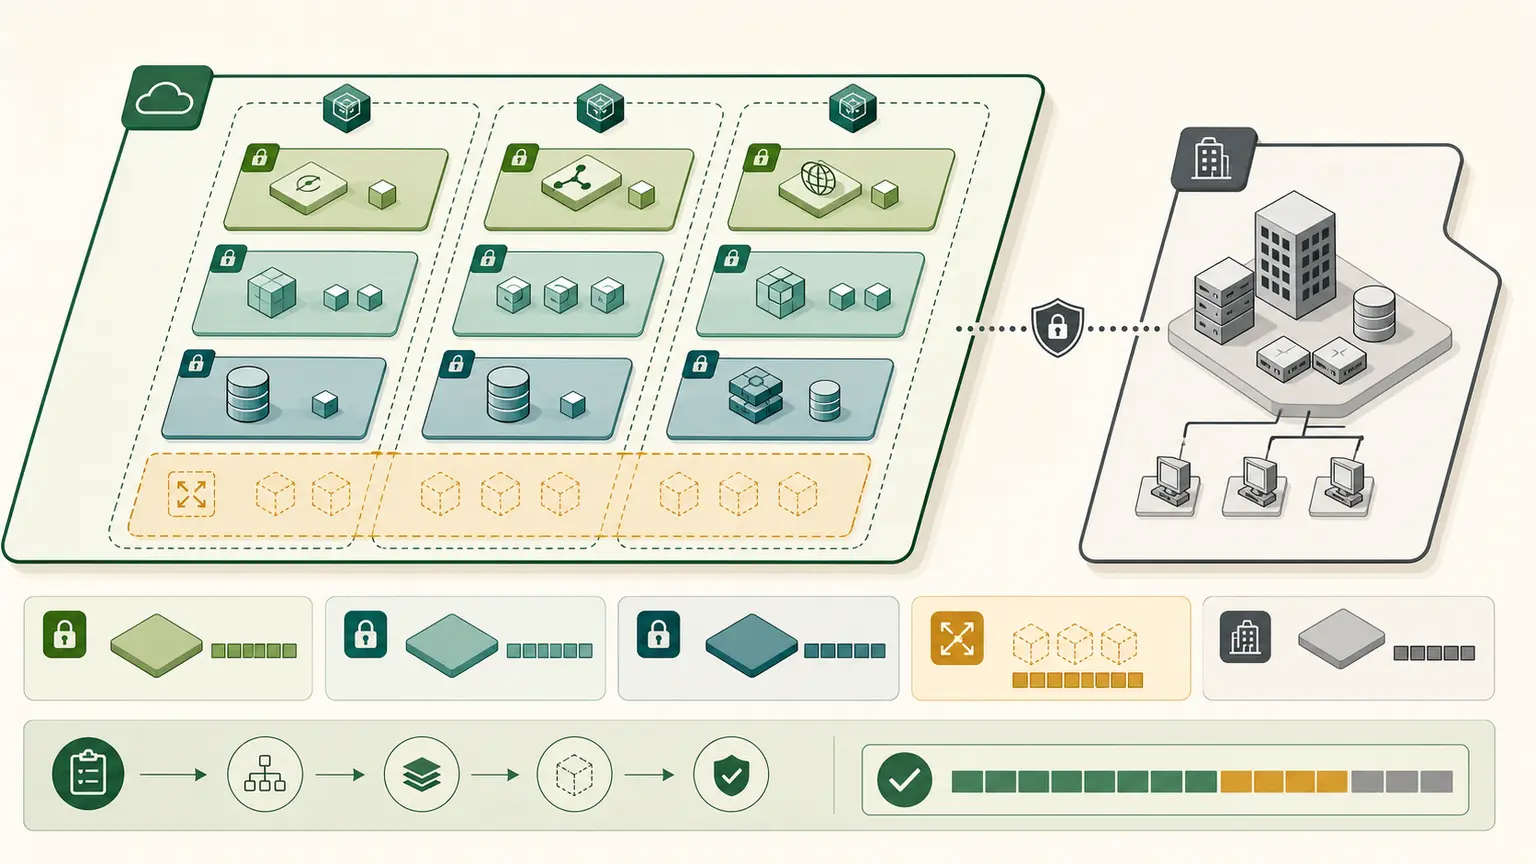
The problem
A team uses Create the VPC, subnets, route tables, internet gateway, security group, and NACL as a label or Console setting without proving the identity, scope, behavior, failure boundary, cost, or operational result. The configuration appears complete but the real requirement remains untested.
Final outcome
The learner will inspect, explain, test, and document Create the VPC, subnets, route tables, internet gateway, security group, and NACL. The submission must connect the Console and CLI view to the same AWS control, state what the evidence proves, diagnose one likely failure, and make a requirement-based architecture decision.
Learning outcomes
You will be able to:
- explain build order;
- explain exact network;
- explain public classification;
- explain security group;
- explain nacl;
- distinguish successful configuration from successful workload behavior;
- preserve redacted evidence and complete the stated cleanup or retention decision.
Mental model
requirement
   -> identity and permission
   -> account, Region, and resource scope
   -> configuration or request
   -> observable state
   -> workload result
   -> failure evidence
   -> cleanup or controlled retention
Never begin with a create button or a copied command. Start with the result that must be proven and the boundary that must remain protected.
Core facts
| Concept | What it means in practice |
|---|---|
| Build order | Create VPC, subnets, internet gateway attachment, route tables and associations, security group, then custom NACL only after reviewing default behavior. |
| Exact network | Use nw-p04-vpc 10.42.0.0/16 and the four approved /24 subnet ranges without overlap. |
| Public classification | A subnet becomes public for IPv4 when its effective route table sends internet destinations to an attached internet gateway. Auto-assign public IPv4 is a separate setting. |
| Security group | Create nw-p04-ec2-sg with no inbound rules and the reviewed outbound rule required for later Session Manager and package access. |
| NACL | Use stateless rules in both directions. Preserve return ephemeral ports and avoid replacing the working default association until the custom rules are verified. |
| Cost and cleanup | VPC, subnets, route tables, IGW, SG, and NACL have no ordinary hourly resource charge, but later attached services do. Cleanup follows dependency order. |
How to reason about it
Build one layer at a time and compare Console with CLI after every action. Never paste discovered IDs without verifying their VPC and Region. Tag every object with Project=NitWings-P04 and Environment=Lab.
The lab retains the network for AWS 061-080. It is not cleaned immediately unless a validation gate fails. The resource ledger must show retained status and final deletion owner.
Use the following decision table as a starting point, then change the answer when the scenario changes.
| Requirement | Preferred direction | Why |
|---|---|---|
| Public subnet route | 0.0.0.0/0 to project IGW | It provides an internet path only for addressed and permitted interfaces. |
| Private subnet route | Local route only in this stage | No NAT cost or unintended egress. |
| Instance management ingress | None | Session Manager will use outbound HTTPS. |
| Custom NACL | Documented allow rules plus final deny | Stateless return traffic is explicit. |
Prerequisites, permissions, Region, and cost
Run this lesson as the approved non-root course identity. Begin with aws sts get-caller-identity, confirm the private account record, and set the fixed project Region before any regional query. IAM resources are global within an account, while STS endpoints and the services reached by an identity can be regional.
Use only the read or change actions required for this lesson. An AccessDenied result is evidence to analyse, not permission to switch to root or attach AdministratorAccess. Record the action, resource, principal type, request context, and smallest justified correction.
The listed cost tier is T1 - free or near-free with immediate cleanup. Free Tier eligibility and credits are account-specific. Before a mutating lab, identify every resource that can charge, estimate its duration, start a timer, and write the reverse cleanup order. A budget reports cost after billing data arrives and is not a real-time stop control.
AWS Management Console method
- Open VPC, Create VPC, choose VPC only, and create nw-p04-vpc with 10.42.0.0/16.
- Create four subnets with the approved names, CIDRs, and two Availability Zones, then create and attach nw-p04-igw.
- Create public and private route tables, associate each subnet, create nw-p04-ec2-sg and nw-p04-nacl, then verify every effective association before retention.
For every step record the service page, selected account and Region, exact object, visible state, and why that state matters. A Console label or green status is not enough unless it is tied to the final workload outcome.
AWS CLI or API evidence
Inventory every project network object by Project tag.
aws ec2 describe-vpcs --region ap-south-1 --filters Name=tag:Project,Values=NitWings-P04
aws ec2 describe-subnets --region ap-south-1 --filters Name=tag:Project,Values=NitWings-P04
aws ec2 describe-route-tables --region ap-south-1 --filters Name=tag:Project,Values=NitWings-P04
Expect one VPC, four non-overlapping subnets, explicit associations, one attached IGW, and no NAT gateway. IDs must be copied into the private ledger.
Before running the command, replace every placeholder, explain each option, and decide whether the operation is read-only or mutating. Capture the exit code immediately. Redact account IDs, ARNs, public addresses, request identifiers, and personal data before sharing.
The CLI and Console are clients of AWS APIs. Matching state across them increases confidence, but neither substitutes for data-plane or application verification.
Practical work
Execute the approved P04 plan in ap-south-1. Pause after each resource and record ID, state, effective association, route, rule, and cost class. Do not launch EC2 yet. Retain only the validated network and update the cleanup ledger with its dependency order.
The evidence package must include:
- non-root principal type, account verified privately, and Region;
- exact intended and observed state;
- one Console observation and the matching CLI or API result;
- one successful result and one denied, failed, or counterexample result;
- what each result does not prove;
- cost state and elapsed lab time;
- cleanup evidence or a named retained-state owner and next lesson.
Verification standard
Use three levels of proof:
- Control plane: the object or policy exists with the intended configuration.
- Data plane or behavior: the request, packet, session, storage path, or application does what the requirement states.
- Operations: monitoring, failure diagnosis, cost, ownership, and cleanup are known.
A control-plane response can precede final readiness. Use waiters or state polling where supported, then test the actual behavior. If a request times out, do not assume it failed. Inspect state and use documented idempotency before retrying a mutation.
Troubleshooting method
| Symptom | Evidence first | Smallest safe response |
|---|---|---|
| command cannot authenticate | credential source, expiry, caller preflight | restore approved temporary login |
| access is denied | action, resource, principal, all policy layers | correct only the missing or conflicting control |
| object appears missing | account, Region, filters, pagination, permission | align scope before creating anything |
| configured state exists but behavior fails | route, identity, dependency, logs, service state | test the next boundary in the path |
| cleanup is blocked | dependency inventory and owning service | remove dependants in reviewed reverse order |
Keep the original symptom and timestamp. State one hypothesis, make one reversible change, repeat the original test, and record rollback. Never open a management port to the world, expose credentials, disable TLS verification, format an unknown disk, or add broad permissions as a generic fix.
Architecture and certification decisions
Professional-level questions provide competing valid features. Identify the requirement that decides between them: human or workload identity, same-account or cross-account access, regional or zonal scope, stateful or stateless filtering, durable or ephemeral data, latency, RTO/RPO, cost, or operational ownership.
Explain why the selected option fits and why each plausible alternative fails one stated requirement. Do not rely on feature memorization or reproduce protected certification questions.
Knowledge check
- Does an IGW route assign a public IPv4?
Expected direction: No. Address assignment is separate.
- Are security groups stateless?
Expected direction: No. They are stateful.
- Why check both NACL directions?
Expected direction: NACLs are stateless.
- When is the network deleted?
Expected direction: After AWS 080 or immediately after a failed build gate.
Cost, cleanup, and retained state
Retain only the state explicitly required by the next P04 lesson and record it in the private resource ledger.
Cleanup evidence includes the final state query, not only a successful delete response. Search related resources, other Regions used by the lab, retained storage, public IPv4 addresses, logging destinations, and service-managed dependencies. Schedule a later billing review because cost data can lag.
Completion gate
Pass when the practical artifact explains the real problem, matches Console and CLI evidence, answers every knowledge check, diagnoses one failure without broadening access, records cost, and proves cleanup or approved retention. The learner must defend one decision orally and name the requirement that would change it.