
AWS 171: Architecture: choose Route 53, CloudFront, Global Accelerator, WAF, and Shield
Why this lesson matters
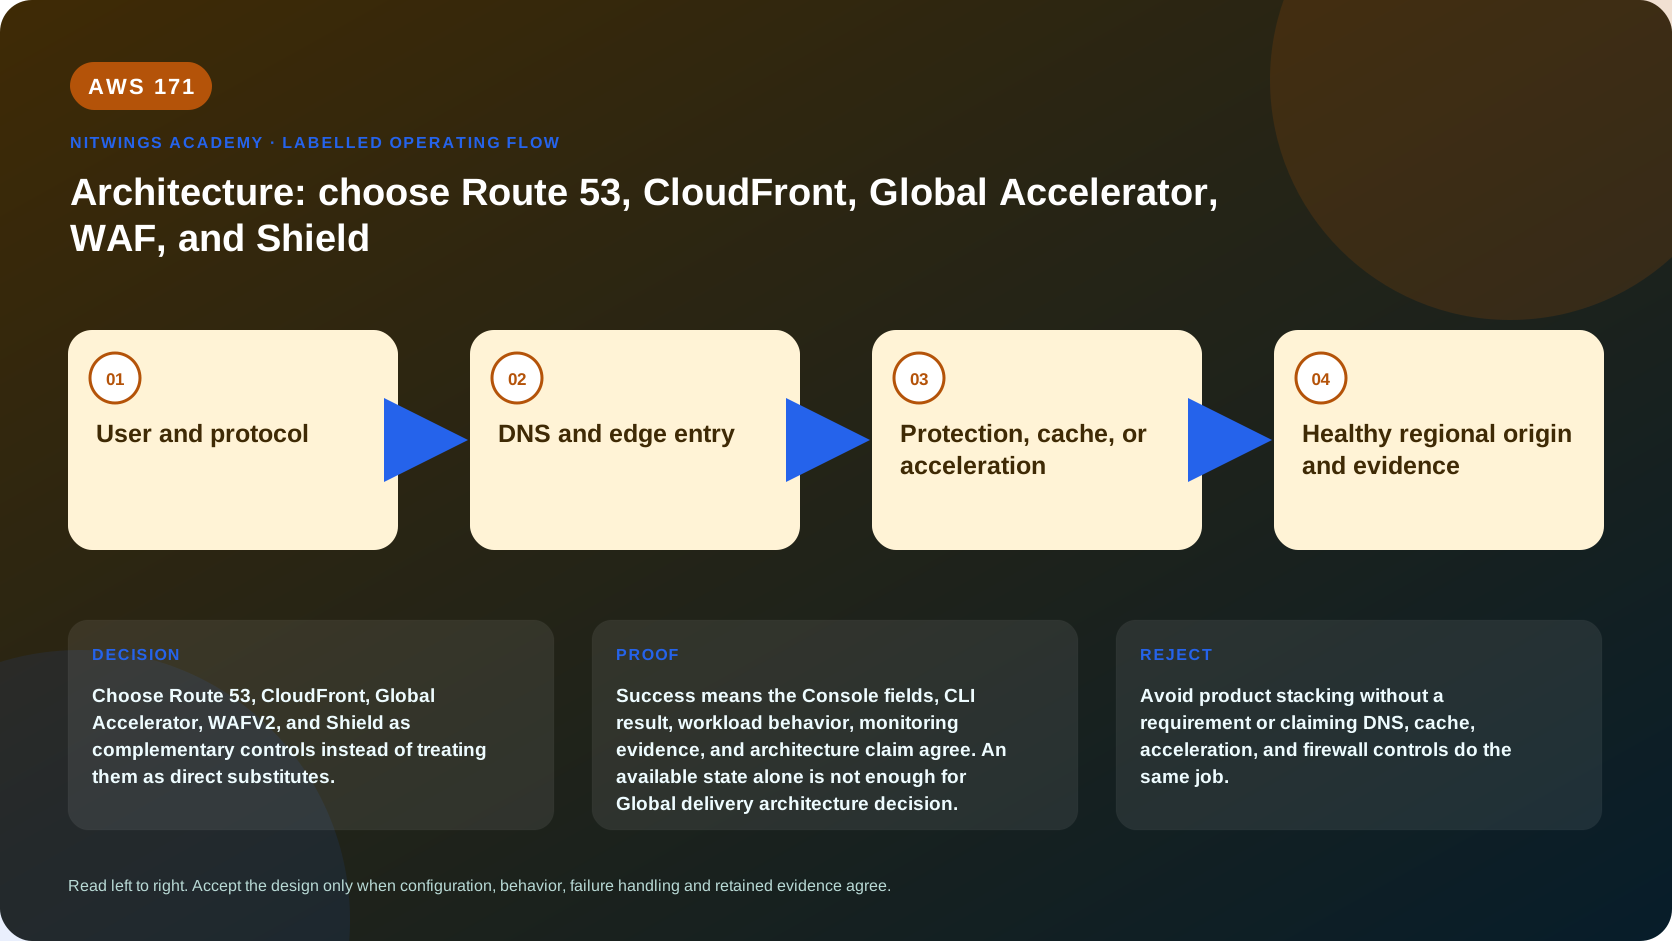
Choose Route 53, CloudFront, Global Accelerator, WAFV2, and Shield as complementary controls instead of treating them as direct substitutes.
These services are usually layers, not alternatives: Route 53 publishes/discovers names, CloudFront proxies and caches HTTP, Global Accelerator accelerates TCP/UDP behind static anycast IPs, WAF filters supported HTTP requests and Shield mitigates DDoS. Use only the layers whose measurable requirement exceeds their cost and failure complexity.
What you will be able to do
By the end, you can:
- explain architecture: choose route 53, cloudfront, global accelerator, waf, and shield in plain language;
- locate the current service controls in the AWS Management Console;
- run the matching CloudShell or AWS CLI queries and explain every important field;
- draw the identity, network, data, failure, and monitoring path;
- choose the service from requirements and reject it when those requirements are absent;
- diagnose a failed or misleading result from evidence;
- state the cost owner and prove cleanup or a no-create result.
Before you start
- Use a personal AWS account only when its owner has approved the lesson. Do not use the root user for daily work.
- CloudShell is the default command environment. AWS028 explains CloudShell; AWS029 and AWS030 explain local AWS CLI installation and profiles.
- The course example Region is
ap-south-1. Global services and services with a required control Region are called out in their commands. - Run
aws sts get-caller-identityprivately. Redact the account number before sharing evidence. - Never paste access keys, passwords, secret values, private object data, presigned URLs, or full account-specific ARNs into a submission.
- This is a no-create lesson. Every Console action and AWS CLI command is read-only. Create the practical artifact locally.
- Console wording can change. Use the Console service search if a menu label has moved, then confirm the current field in the official documentation.
The core model
| Question | What it means in this lesson |
|---|---|
| Purpose | Choose Route 53, CloudFront, Global Accelerator, WAFV2, and Shield as complementary controls instead of treating them as direct substitutes. |
| Scope and boundary | The learner must identify the account and Region scope, resource boundary, identity path, data or network path, failure behavior, observability, and cleanup ownership for Global delivery architecture decision. |
| Evidence of success | Success means the Console fields, CLI result, workload behavior, monitoring evidence, and architecture claim agree. An available state alone is not enough for Global delivery architecture decision. |
| Cost model | Requests, running capacity, storage, logs, data transfer, retained state, and optional features must be priced for the exact design. |
| Safe rejection rule | Avoid product stacking without a requirement or claiming DNS, cache, acceleration, and firewall controls do the same job. |
How the request flows
+----------------------+
|  User and protocol   |
+----------------------+
           |
           v
+----------------------+
|  DNS and edge entry  |
+----------------------+
           |
           v
+--------------------------------------+
|  Protection, cache, or acceleration  |
+--------------------------------------+
                   |
                   v
+----------------------------------------+
|  Healthy regional origin and evidence  |
+----------------------------------------+
For Global delivery architecture decision, the important boundary is this: The learner must identify the account and Region scope, resource boundary, identity path, data or network path, failure behavior, observability, and cleanup ownership for Global delivery architecture decision. Success means the Console fields, CLI result, workload behavior, monitoring evidence, and architecture claim agree. An available state alone is not enough for Global delivery architecture decision. That is why the lesson pairs the Console with CLI output and a practical artifact. One interface may hide a field, use a cached view, or be scoped differently. Matching evidence is stronger than a screenshot alone.
Architecture decision table
| Situation | Direction | Reason |
|---|---|---|
| Requirement matches | Combine only the layers required by protocol, latency, caching, address, security, and recovery needs. | Select only after scope, behavior, security, recovery, operations, and price evidence agree. |
| Requirement does not match | Avoid product stacking without a requirement or claiming DNS, cache, acceleration, and firewall controls do the same job. | Rejecting an attractive service is a valid architecture result. |
| No create permission or cost approval | Use supplied evidence and local design work | Learning does not depend on creating an hourly resource. |
| Existing resource is unknown or unowned | Inspect only, then stop | Never change or delete a resource merely because it resembles a course example. |
Layer selector
| Requirement | Control | What it does not do |
|---|---|---|
| domain delegation, records, policy-based DNS answer, hybrid resolution | Route 53 authoritative/Resolver | proxy traffic, cache HTTP objects or terminate application TLS |
| global HTTP(S) proxy/cache, origin protection, edge logic | CloudFront | provide arbitrary TCP/UDP acceleration or replicate origin truth |
| fixed global IP and optimized TCP/UDP path to healthy Regional endpoints | Global Accelerator Standard | cache content, host DNS or protect every application-layer exploit |
| deterministic user-to-game-server mapping | GA custom routing | health-check/fail over destinations automatically |
| managed L7 request filtering/rate/bot rules on supported resources | WAFV2 | secure direct origin bypass, inspect arbitrary L4 traffic or fix app authorization |
| baseline DDoS mitigation | Shield Standard | provide DRT/cost protection or enroll every advanced resource |
| enhanced DDoS detection/response/cost protection for enrolled resources | Shield Advanced | eliminate capacity/health/runbook responsibilities |
A common static site path is Route 53 alias → CloudFront + WAF/Shield → OAC-protected S3. A dynamic API can use Route 53 → CloudFront + WAF → Regional ALB/API origins with safe caching or no caching. A TCP game service can use Route 53 name → Global Accelerator → NLB/EC2, with application TLS and Shield/endpoint controls. Active-passive DNS may use Route 53 health; fast new-connection IP routing may use GA; neither synchronizes databases.
Define where DNS, viewer/application TLS, authentication, WAF, DDoS, cache, health and origin authorization terminate. Hide origins from direct access. Decide IPv4/IPv6, client-IP preservation, data residency and log location. Cross-border edge processing/caching can have compliance implications even when the origin Region is fixed.
Availability calculations include DNS TTL/resolver, edge/accelerator health detection, connection lifetime, endpoint capacity, origin data RPO and application failback. Test all-unhealthy behavior and secondary capacity. Cost includes hosted zones/queries/health checks/Resolver endpoints, CloudFront requests/egress/functions/logs/invalidation/Origin Shield, GA hourly/data premium, WAF ACL/rules/requests/managed groups/logs and Shield Advanced subscription/data/resource charges.
AWS Management Console, step by step
Sign in with the normal non-root learning identity. Write the expected starting state before opening the service.
- Use the Console service search and open Route 53, CloudFront, Global Accelerator, WAF, and Shield inventories; confirm the account and Region before reading the page.
- Inspect the supplied or owned resource's status, configuration, permissions, networking, encryption, monitoring, tags, and dependencies without changing it.
- Open the related metrics, logs, events, or history view and record one timestamped signal that would prove or disprove the expected behavior.
- Return to the resource list, clear filters, and record the final inventory. On the read-only track, do not choose Create, Save, or Delete.
CloudShell and AWS CLI, step by step
Start with a known caller and Region:
export AWS_DEFAULT_REGION="ap-south-1"
aws sts get-caller-identity --query Arn --output text
aws configure list
Redact the account part of the ARN in shared evidence. Now run the topic queries:
aws route53 list-hosted-zones --query 'HostedZones[].Name' --output text
aws cloudfront list-distributions --query 'DistributionList.Items[].DomainName' --output text
aws globalaccelerator list-accelerators --region us-west-2 --query 'Accelerators[].Name' --output text
aws wafv2 list-web-acls --scope REGIONAL --region ap-south-1 --query 'WebACLs[].Name' --output text
Expected interpretation
The services sit at different layers: DNS answer, HTTP edge cache, network acceleration, HTTP filtering, and DDoS protection. A design may use several but must justify each.
Practical work
Submit a global-delivery ADR for static assets, dynamic API, gaming TCP, and active-passive recovery. Map each packet, DNS, TLS, health, security, logging, failover, and charge boundary.
For each workload reject two plausible layers, draw normal/bypass/failure paths and calculate latency/cost. Tabletop origin bypass, stale cache/private-data leak, WAF false positive, DDoS/flash crowd, unhealthy Region, all endpoints unhealthy, DNS cache delay and database lag. Include rollout/rollback for DNS, distribution, accelerator dial and WAF Count→Block.
Diagnose this topic from its own evidence
Locate the first service that saw the request: authoritative DNS answer/TTL, GA flow/endpoint health, CloudFront request/cache/WAF action, origin log. If no layer has evidence, investigate client DNS/network/TLS. Avoid adding layers to mask the fault. A cache hit cannot prove origin health; healthy GA endpoint cannot prove business correctness; WAF block cannot appear in origin logs.
Cost and cleanup
Requests, running capacity, storage, logs, data transfer, retained state, and optional features must be priced for the exact design.
Knowledge check
- What operational purpose is this lesson solving?
Expected direction: Choose Route 53, CloudFront, Global Accelerator, WAFV2, and Shield as complementary controls instead of treating them as direct substitutes.
- Which scope or ownership boundary must be proved first?
Expected direction: The learner must identify the account and Region scope, resource boundary, identity path, data or network path, failure behavior, observability, and cleanup ownership for Global delivery architecture decision.
- What evidence is strong enough to accept the result?
Expected direction: Success means the Console fields, CLI result, workload behavior, monitoring evidence, and architecture claim agree. An available state alone is not enough for Global delivery architecture decision.
- Which tempting design or shortcut must be rejected?
Expected direction: Avoid product stacking without a requirement or claiming DNS, cache, acceleration, and firewall controls do the same job.
- Which cost dimensions and retained resources need an owner?
Expected direction: Requests, running capacity, storage, logs, data transfer, retained state, and optional features must be priced for the exact design.
Lesson acceptance
Pass when every selected layer has one explicit requirement, cost and owner; packet/DNS/TLS/identity/cache/health paths are accurate; origin bypass and recovery are tested; and two attractive but unnecessary services are rejected. Fail if products are direct synonyms, failover implies data replication, or security relies on a public bypassable origin.