
AWS 412: Config conformance packs and automated remediation
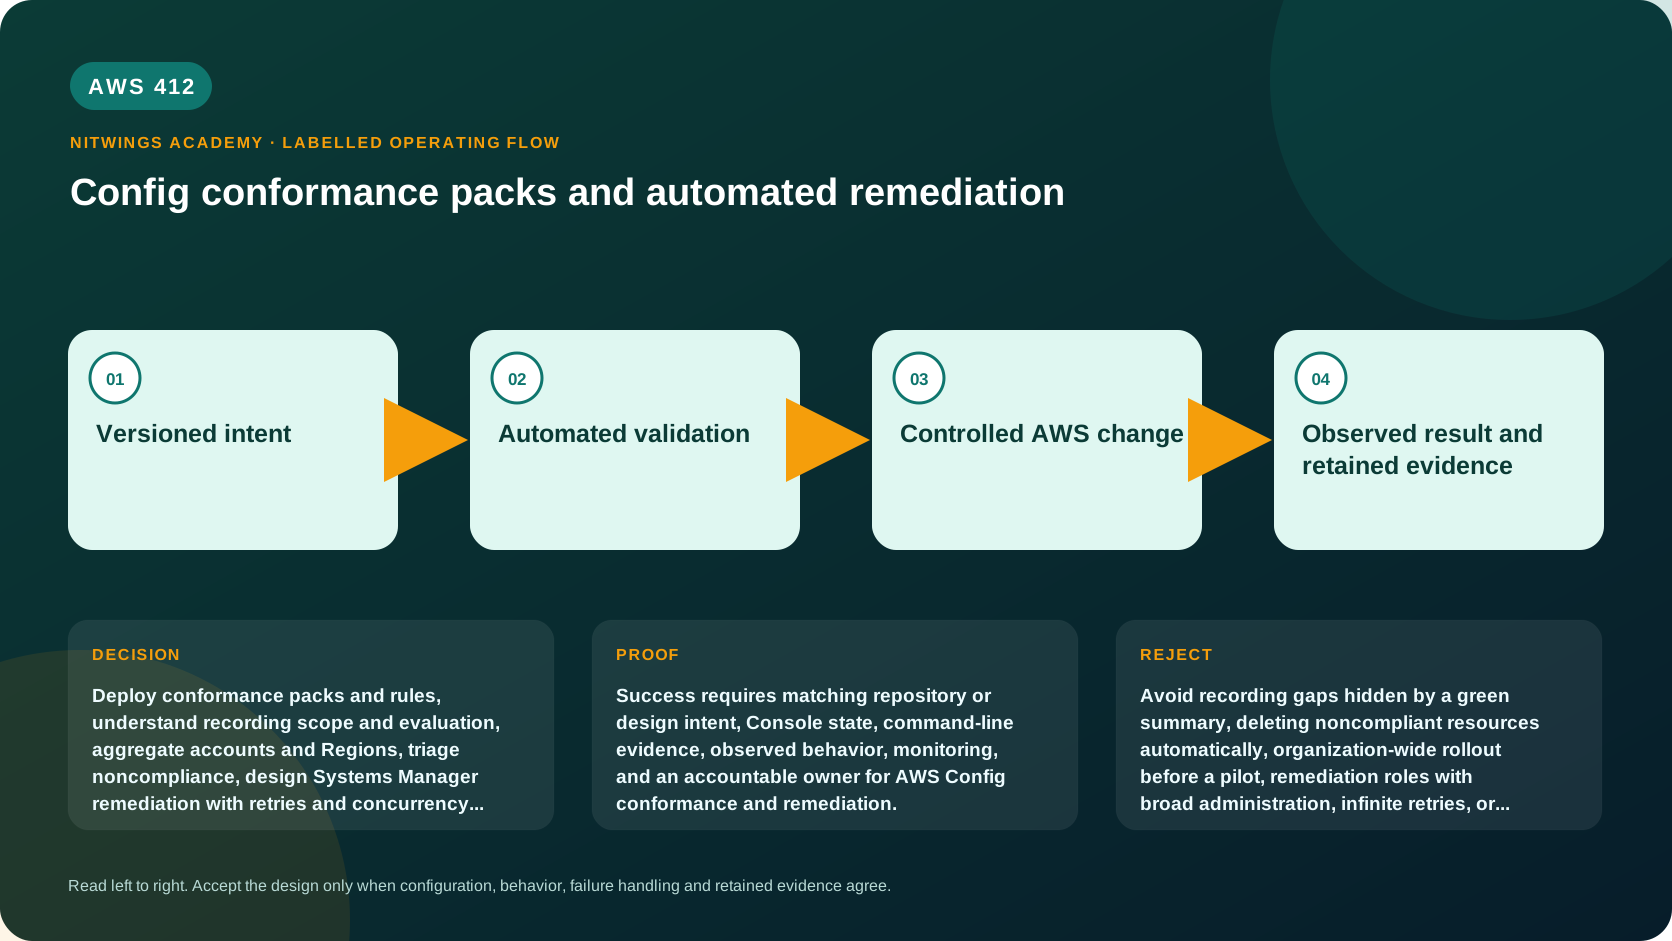
Why this lesson matters
AWS Config records supported resource configuration and evaluates rules. A conformance pack deploys a collection of rules and optional remediation configuration, but does not guarantee that recording is complete, every policy is suitable, or remediation is safe. Architects must prove scope, evaluation semantics, ownership, exceptions and post-change outcomes.
Recording, rules and packs
The configuration recorder, delivery channel and resource recording strategy are the evidence foundation. Before trusting compliance, verify account/Region coverage, recorder status, included/excluded resource types, global-resource handling, delivery errors and history retention. NOT_APPLICABLE, INSUFFICIENT_DATA or an absent resource is not equivalent to COMPLIANT.
Rules can be AWS managed or custom Lambda/Guard based and can evaluate on configuration changes, periodic schedules or both according to rule support. Trigger and scope determine when a resource is checked. Conformance packs package rule definitions, parameters and optional remediation settings for consistent deployment; they do not bundle historical evidence or solve conflicting rules automatically.
| Layer | Evidence | Failure to detect |
|---|---|---|
| Organization/account/Region deployment | Pack/rule inventory | Missing accounts or Regions |
| Recorder scope/status | Recorded resource types and errors | Compliance blind spots |
| Rule trigger/scope/parameters | Exact evaluation contract | Wrong or late decisions |
| Evaluation result/timestamp | Resource-specific state | Stale status |
| Remediation execution | Automation ID, target and result | Failed/partial mutation |
| Post-evaluation/user test | Desired and workload outcome | API success without compliance |
Organization conformance packs need delegated/management-plane permissions and member-account execution roles/service access according to the chosen model. New accounts and Regions require reconciliation. Aggregate compliance centrally for governance, but retain local diagnosis and remediation evidence.
Safe automated remediation
Config remediation invokes a Systems Manager Automation document with parameters mapping the noncompliant resource and an assumed automation role. Automatic remediation can run when Config evaluates noncompliance; manual remediation requires explicit invocation. Use versioned documents, exact resource types, least privilege, idempotent steps, concurrency/error controls and a maximum-attempt/exception path.
The resource may already be compliant by execution time, so the runbook re-reads authoritative state before mutation. Classify controls: safe automatic correction, automatic evidence/ticket only, human-approved correction, or detect-only. Destructive, availability-affecting, data-policy or ambiguous ownership changes should not be blindly automated.
Remediation success means the intended resource state and user/security outcome are verified, followed by a fresh Config evaluation. Config can show stale noncompliance after the resource changes until reevaluation, and an automation execution can succeed while the rule remains noncompliant because the runbook changed the wrong property. Track both states.
Exceptions need resource/control scope, business rationale, compensating controls, owner, approval, creation/expiry and reevaluation. Do not encode permanent exceptions by weakening the global rule parameter. Separate approved exceptions from unsupported/not-recorded resources and alert before expiry.
Change, rollback and evidence
Test pack changes in an isolated account with representative compliant/noncompliant/unsupported resources. Preview parameter and remediation impact, deploy to canary accounts/OUs/Regions, monitor evaluation/remediation volume, then expand. Keep previous template/version and know whether rollback removes resources, rules or only future behavior. Avoid two controls fighting over the same property.
~~~bash aws configservice describe-configuration-recorder-status aws configservice describe-conformance-packs aws configservice describe-conformance-pack-status aws configservice get-conformance-pack-compliance-summary --conformance-pack-names PACK aws configservice describe-remediation-configurations --config-rule-names RULE aws configservice describe-remediation-execution-status --config-rule-name RULE ~~~
Maintain an evidence ledger: pack/template hash, rule/parameter version, account/Region, recorder proof, resource configuration item, evaluation, exception, automation execution, CloudTrail change identity, post-state and owner. Protect the Config delivery bucket, encryption key and aggregator access. Alert on recorder stop, delivery failure, rule/pack deletion, parameter/remediation change, execution failure, exception expiry and persistent recurrence.
Workshop and failure analysis
Given four accounts and three Regions, find recording and deployment gaps, evaluate twelve resources under six rules, and distinguish compliant, noncompliant, not applicable, insufficient data and missing. Design a conformance pack and remediation matrix, diagnose six supplied Automation histories, and create canary/rollback plus exception procedures.
Test 22 failures: recorder stopped, resource type excluded, global scope wrong, Region missed, new account absent, periodic rule assumed immediate, stale evaluation, NOT_APPLICABLE treated compliant, parameter type wrong, custom rule times out, pack deploy partial, conflicting rules, broad automation role, wrong resource mapping, non-idempotent retry, concurrency too high, success without post-state, resource changes before action, exception never expires, rollback deletes evidence, delivery bucket writable broadly, and persistent drift not measured.
Cost and acceptance
Price recorded configuration items, rule evaluations, conformance pack evaluations, remediation/SSM/Lambda, aggregation and evidence storage. This lesson creates nothing. Submit coverage proof, pack/template, rule semantics, remediation classification/runbooks, exception register, rollout/rollback, evidence ledger and all diagnoses. Pass requires complete recording proof, safe bounded remediation and fresh evaluation plus outcome verification.