Email Bounce Handling for Marketers: Classify and Act Safely
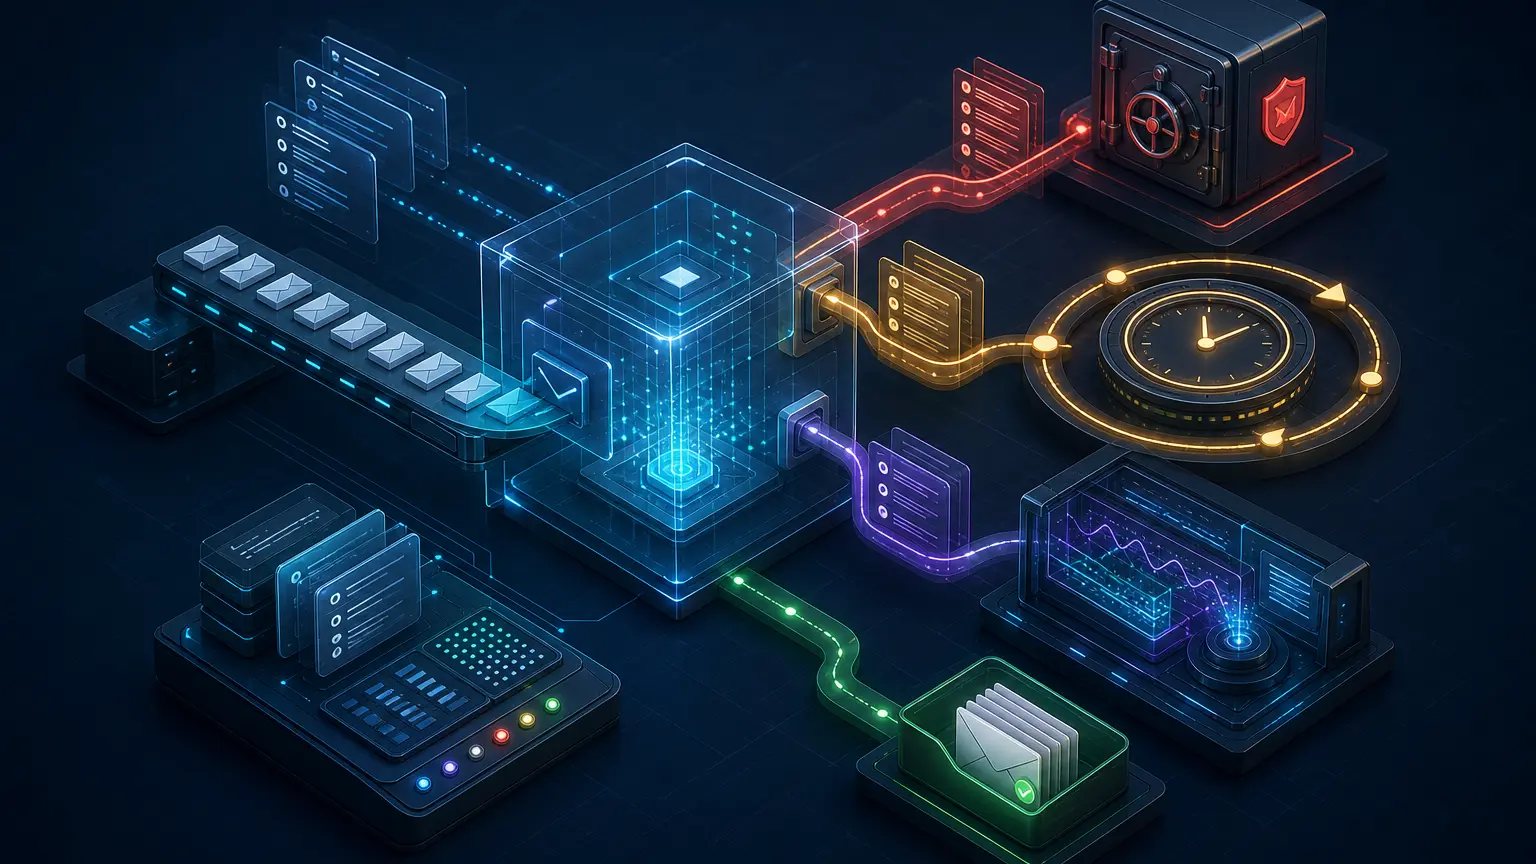
A bounce is evidence that one delivery attempt did not complete as expected. It is not automatically proof that an address is bad, a campaign is poor, or a recipient should disappear from every future send. Safe bounce handling starts with the SMTP reply or delivery status notification, identifies what failed, and applies an action at the right scope.
Use an evidence-led operating process shared by marketers, deliverability teams, and mail-platform engineers. Fixed percentage claims and a simple hard-versus-soft workflow can suppress valid recipients when authentication, policy, content, routing, or provider controls caused the failure.
Start with the delivery event, not a hard or soft label
Most campaign dashboards reduce failures to “hard” and “soft” bounces. Those labels are convenient for summaries, but they hide information needed for a safe decision. Before assigning a label, establish where the failure occurred.
- Synchronous SMTP rejection: the receiving system rejects the recipient or message during the live SMTP conversation. The sending MTA still owns the message and records the reply.
- Asynchronous delivery status notification: a system accepts the message first and later returns a machine-readable or human-readable failure report. The original SMTP acceptance is therefore not the final outcome.
- Local expiration: the sending system keeps retrying a temporary failure, reaches its queue lifetime or retry limit, and generates a final failure event even though the last remote status may still be temporary.
- Complaint, unsubscribe, or spam-folder placement: these are important outcomes, but they are not bounces and should not be rewritten as SMTP failure categories.
SMTP acceptance also does not prove inbox placement, display, reading, or a person taking action. Keep delivery, placement, complaint, unsubscribe, and engagement events distinct so one metric cannot impersonate another.
Preserve the full SMTP and DSN evidence
The Delivery Status Notification format in RFC 3464 was designed for machine processing. A DSN can contain per-message fields and a separate group of fields for each affected recipient. The action and status fields are both important: a message with a 4.x status can eventually have an action of failed after the sending queue stops retrying.
| Evidence | What it answers | Why it matters |
|---|---|---|
| SMTP reply and enhanced status code | What the remote or local system reported | Provides the first classification signal without replacing the diagnostic text |
| SMTP phase | Whether failure occurred at connection, greeting, MAIL FROM, RCPT TO, DATA, or after acceptance | Separates recipient rejection from message, policy, protocol, or connection failure |
| DSN action | Whether the message was delayed, failed, delivered, relayed, or expanded | Shows what happened to this delivery event, including local queue expiration |
| Final recipient and original recipient | Which envelope recipient was affected and whether it was rewritten | Prevents display-address or forwarding changes from being treated as a different person |
| Reporting MTA, remote MTA, and receiving MX | Which systems produced and received the attempt | Supports provider-level and route-level analysis |
| Raw diagnostic code | What the responding system said in its own words | Provider text often distinguishes invalid recipients from policy, reputation, size, or authentication failures |
| Attempt time, queue age, and retry history | When the issue began and how long it persisted | Separates one transient event from a sustained delivery problem |
| Message, campaign, stream, tenant, source IP, and return path | What traffic produced the event | Allows containment without applying a global action to unrelated mail |
Store the normalized fields used for reporting and keep the original response or DSN payload for investigation. Do not keep only a vendor label. When a classification rule changes, the raw evidence lets the team reprocess historical events instead of guessing what the source once said.
Read enhanced status codes as a hierarchy
RFC 3463 enhanced mail system status codes use the form class.subject.detail. The first digit gives the broad result, the second identifies the subject area, and the third adds detail. Read all three with the SMTP phase and diagnostic text.
| Signal | General meaning | Initial handling |
|---|---|---|
2.x.x | Success | Record the delivery-stage success. Do not convert it into proof of inbox placement or reading. |
4.x.x | Persistent transient failure | Let the sending MTA retry according to its queue policy while monitoring duration and concentration. |
5.x.x | Permanent failure for the current attempt or current message form | Do not retry unchanged. Choose the next action from the subject, detail, phase, and diagnostic text. |
x.1.x | Addressing status | Check whether the specific mailbox, domain, or address syntax failed. |
x.2.x | Mailbox status | Distinguish disabled, full, over-quota, or message-specific mailbox limits. |
x.3.x | Mail system status | Investigate receiving-system availability, configuration, capacity, or message-size limits. |
x.4.x | Network and routing status | Investigate DNS, connection, routing, congestion, and transport paths. |
x.5.x | Mail delivery protocol status | Inspect protocol commands, replies, implementation behavior, and gateway translation. |
x.6.x | Message content or media status | Review conversion, supported content, encoding, and message structure. |
x.7.x | Security or policy status | Investigate authorization, authentication, reputation, content policy, rate controls, or account restrictions. |
A 5.x response is not synonymous with “mailbox does not exist.” For example, 5.1.1 is a bad destination mailbox address, while 5.7.1 concerns authorization or policy. Google documents current Gmail SMTP errors including 5.7.x failures for authentication and unsolicited-volume policy. Microsoft likewise documents that Exchange Online NDR codes expose policy, authorization, routing, recipient, and configuration causes. A global recipient suppression based on the first digit alone can therefore discard a valid address while leaving the real sender problem untouched.
Map evidence to an action at the correct scope
The safest action is the narrowest one supported by the evidence. Recipient validity, domain routing, provider throttling, sender authentication, message construction, and local infrastructure belong to different scopes.
| Observed pattern | Likely scope | Safe first action |
|---|---|---|
5.1.1 at RCPT TO with clear unknown-user text | One recipient address | Stop attempts to that address and create a durable invalid-recipient suppression with the evidence retained. |
| Invalid or nonexistent destination domain | Address or domain | Stop the affected destination, confirm DNS and acquisition data, and provide a correction path if the address came from a user. |
4.2.2 mailbox full | One mailbox, temporary | Allow normal queue retries. If the queue expires, use a temporary hold or review policy rather than declaring the address nonexistent. |
4.4.x connection, DNS, or routing failure across many recipients | Route, domain, provider, network, or infrastructure | Keep recipient records intact and investigate the transport path. |
4.7.x deferral concentrated at one provider | Provider, stream, IP, domain, or rate | Contain or slow the affected traffic, inspect reputation and policy signals, and coordinate with MTA operations. |
5.7.x authentication or sender-policy rejection | Sending identity, message stream, tenant, or provider | Hold the affected traffic, repair the identity or policy cause, and test before resuming. Do not mark every recipient invalid. |
5.3.4, 5.6.x, or explicit size or content conversion error | Message or sending pipeline | Correct the message structure, encoding, or size and submit a materially fixed version if appropriate. |
| Local queue expires after repeated 4.x replies | Delivery event plus its underlying temporary scope | Record the final event and the last transient evidence separately. Investigate duration and concentration before changing recipient state. |
Provider wording can be inconsistent, customized, or forwarded through an intermediate gateway. Build classifications from several signals and maintain an “unknown or conflicting” queue for review. An imperfect review path is safer than a confident destructive action based on a weak regex.
Let the MTA own transport retries
SMTP in RFC 5321 distinguishes transient 4xx replies from permanent 5xx replies. The sending MTA should manage queueing, retry intervals, destination concurrency, and expiration for transient transport failures. A marketing platform should not launch duplicate campaign sends while the same message remains in the MTA queue.
- Retry 4xx outcomes through one controlled queue policy, not through repeated campaign jobs.
- Keep the original message identity and delivery attempt history correlated.
- Use backoff and provider-aware rate controls. Immediate repeated attempts can worsen congestion or policy enforcement.
- Set a documented queue lifetime appropriate to the message. A password code that expires in ten minutes and a non-urgent account notice should not have identical usefulness windows.
- Stop retrying an unchanged message after a true 5xx response, but route the event to the action appropriate for its cause.
- Distinguish “temporary remote response” from “final local outcome after retry exhaustion” in reporting.
A fixed rule such as “retry twice” or “suppress after three soft bounces” ignores timing, message type, provider behavior, and cause. Ten deferrals in three minutes are not equivalent to three separate queue expirations over six months.
Model suppression as state, not deletion
Suppression should prevent unsafe or unwanted sends while preserving the reason, scope, and correction path. It should not delete the contact, erase consent history, or merge unrelated policy decisions into one boolean field.
| State | Typical trigger | Duration and release |
|---|---|---|
| Unsubscribed from marketing | Valid recipient request | Durable for the relevant brand or program unless the person takes a lawful, explicit resubscription action. |
| Complaint suppression | Mailbox-provider complaint or equivalent trusted signal | Immediate marketing stop at the required scope. Keep separate from bounce codes and consent records. |
| Invalid recipient | Strong recipient-specific permanent evidence such as confirmed 5.1.1 | Durable for that address until it is corrected or re-established through an approved ownership process. |
| Temporary recipient hold | Repeated mailbox-full outcomes or a time-bounded recipient issue | Expires or moves to review under a written policy. It must not silently become permanent without new evidence. |
| Provider or route hold | Concentrated deferral, network failure, or provider enforcement | Release after the route is repaired and controlled tests pass. |
| Identity, policy, or message hold | Authentication, authorization, content, size, or stream failure | Release only the repaired identity, stream, or content version after validation. |
| Manual review | Unknown, contradictory, low-confidence, or high-impact evidence | Owned queue with a service level, reviewer, evidence, and auditable decision. |
Each state should record the address or affected object, tenant or brand, message stream, reason code, source event, raw evidence reference, classifier version, creation time, expiry if any, and actor. Consent and suppression are related controls, but they answer different questions. A person may still have a consent record while a misspelled address is suppressed; correcting the address does not invent new consent.
Build a reliable event pipeline
Bounce handling fails when an integration assumes every webhook arrives once, in order, and with the same vocabulary. Treat event intake as a production data pipeline.
- Authenticate webhook requests and restrict ingestion to expected sources.
- Use an idempotency key or stable event identity so retries do not create duplicate suppressions.
- Expect late and out-of-order events. A delayed DSN can arrive after another platform event.
- Correlate envelope recipient, Message-ID, provider message identifier, campaign, tenant, stream, return path, and MTA queue identifier where available.
- Normalize recipient addresses consistently without making unsafe assumptions about case, internationalized domains, aliases, or provider-specific mailbox behavior.
- Store raw evidence securely, minimize unnecessary personal data, restrict access, and apply an explicit retention policy.
- Version parsing and classification rules so an operator can explain why a decision occurred.
Monitor ingestion health as well as bounce rate. Track webhook age, parse failures, unmatched events, duplicates, classifier fallbacks, and the gap between MTA records and application records. A clean dashboard built on missing events is more dangerous than an honest unknown category.
Keep complaints and unsubscribes out of the bounce taxonomy
A complaint says that a recipient or mailbox provider reported a message as unwanted. An unsubscribe says that a recipient wants a defined stream to stop. Neither is a transport failure, even if all three outcomes ultimately prevent another marketing send.
Process trusted complaints quickly under the program and provider requirements. Process unsubscribe requests through the appropriate consent and preference workflow. Keep both in reporting beside bounces, not inside the hard-bounce count. This separation lets the team see whether it has an address-quality problem, a relevance or consent problem, a transport problem, or several problems at once.
Do not use engagement activity to override an unsubscribe, complaint, or strong invalid-recipient event. Opens are incomplete signals, and a previous click does not make a current delivery failure disappear.
Improve acquisition before buying more cleaning
Invalid-recipient control begins where addresses enter the system. A verification vendor can add evidence, but a vendor score does not prove ownership, consent, continued reachability, or future acceptance.
- Validate obvious syntax and domain errors without claiming that syntax proves deliverability.
- Suggest corrections for common domain typos, but require the person to confirm the corrected address.
- Use confirmation when the risk and relationship justify it, especially before granting valuable access or starting a high-frequency stream.
- Record the acquisition source, consent statement, time, brand, expected message type, and relevant proof.
- Avoid purchased, scraped, appended, or unexplained legacy data.
- Give users a clear way to correct an address after a failed operational message.
- Review imports and integrations with the same controls as public forms.
Do not perform abusive SMTP probing or treat a catch-all domain as proof that every mailbox is valid. For a broader treatment of temporary inboxes, aliases, privacy relays, and verification limits, see Disposable E-mail Addresses: Detection Without False Positives. When the issue crosses acquisition, suppression, MTA evidence, and provider behavior, the Email Deliverability service can review the complete path.
Separate recipient, content, identity, and infrastructure failures
A useful operational dashboard does not place every red event under “list quality.” The same campaign can expose several independent systems.
- Recipient failure: the specific destination is invalid, disabled, over quota, or otherwise unable to accept the message.
- Content or message failure: the message is too large, malformed, unsupported, or rejected in its current form.
- Identity and policy failure: SPF, DKIM, DMARC, envelope identity, authorization, reputation, traffic behavior, or provider policy prevents acceptance.
- Infrastructure failure: DNS, routing, TLS, connection, local queue, capacity, credentials, or MTA configuration breaks the path.
- Unknown failure: evidence is missing, contradictory, or too generic for a safe classification.
This separation changes ownership. Marketing may repair acquisition or cadence. The content team may rebuild a message. Deliverability may investigate reputation and provider enforcement. Platform engineers may repair authentication, queues, routes, or event ingestion. A shared classification gives each team a specific failure to solve.
Use marketing controls for the problem they can solve
Authentication, content, throttling, segmentation, engagement, list age, and re-engagement all belong in a healthy email program, but they do not change the same outcome. Apply each control to the evidence it can actually influence.
| Program control | What it can improve | What it does not prove |
|---|---|---|
| Address correction, verification, and confirmed subscription | Prevents obvious typing errors, confirms control of an address, and reduces invalid data entering a list | A vendor score or one confirmation does not guarantee that the mailbox will exist or accept every future message |
| SPF, DKIM, and DMARC | Establishes authorized sending, message integrity, visible-domain alignment, and authentication reporting | Authentication does not clean a list, create consent, or guarantee acceptance and inbox placement |
| Subject, content, HTML, and image review | Improves clarity, accessibility, rendering, message size, and compliance with an identified content or policy requirement | A list of supposedly forbidden promotional words is not a dependable bounce classifier, and a spam-folder result is not a soft bounce |
| Provider-aware throttling | Responds to rate limits, congestion, reputation controls, and concentrated temporary deferrals | Slower sending does not repair an invalid recipient, broken authentication, or malformed message |
| Segmentation by consent, acquisition source, relationship, list age, preference, and message stream | Keeps audience expectations, frequency, relevance, and operational risk visible | Demographic or engagement segments do not establish mailbox validity and should not replace SMTP evidence |
| Inactivity and re-engagement policy | Limits unnecessary marketing pressure and provides a controlled way to confirm whether a person still wants a stream | A missing open does not prove inactivity, and a previous open or click does not override a complaint, unsubscribe, or invalid-recipient event |
| Feedback loops and provider dashboards | Adds complaint, reputation, authentication, and provider-specific context to the investigation | Complaint or reputation signals should not be stored as recipient bounce codes |
Use engagement cautiously. Opens can be created, hidden, or distorted by image blocking, privacy protection, security scanners, and proxying. Clicks, conversions, purchases, account activity, stated preferences, and replies can add context, but no engagement score should reactivate an address that has a valid suppression reason.
For segmentation, begin with the relationship and sending purpose rather than an arbitrary A, B, or C rating. Separate newly confirmed subscribers, established customers, recent purchasers, declared content preferences, inactive marketing subscribers, and recipients of essential operational mail only when the distinction supports a documented decision. A six-month inactivity window may be reasonable for one frequent newsletter and meaningless for a seasonal or annual service. Define the window from the expected cadence and relationship.
Provider dashboards can reveal changes in reputation, authentication, complaint patterns, or delivery errors, but they supplement the SMTP and DSN record. If a campaign is rejected, start with the actual reply. If it is accepted but placed in spam, investigate placement and reputation without relabeling the event as a bounce.
Analyze by provider, stream, and time
A single global bounce percentage can hide a serious incident and can also exaggerate a harmless change in audience mix. Segment the evidence before drawing a conclusion.
- Group by the receiving MX or provider relationship, not only by the visible recipient domain. Many domains share hosted mail infrastructure.
- Separate transactional, lifecycle, promotional, and operational streams. Their audiences, urgency, queue lifetimes, and acceptable controls differ.
- Compare source IP, sending domain, DKIM identity, return path, tenant, template, acquisition source, and list age.
- Use event time and attempt time. A backlog delivered later can distort a report grouped only by campaign creation date.
- Compare rates with counts and sample sizes. One failure among two attempts should not trigger the same response as ten thousand failures in a mature stream.
- Maintain a normal range for each important provider and stream rather than one universal industry benchmark.
Investigate both level and change. A high stable invalid-recipient rate from one acquisition source suggests a quality problem. A sudden provider-specific 4.7.x spike with no audience change suggests transport, reputation, rate, or provider enforcement. The actions are different even if both raise the dashboard bounce line.
Use metrics that point to decisions
| Metric | Useful denominator | Decision it supports |
|---|---|---|
| Recipient-specific permanent failure rate | Unique attempted recipients | Acquisition quality, correction flows, and durable recipient suppression |
| Temporary deferral rate | SMTP delivery attempts, segmented by provider and stream | Rate, reputation, provider, route, and capacity investigation |
| Delivered after retry | Messages that first received a transient reply | Whether queue and retry policy recover temporary failures |
| Queue expiration rate and age | Queued messages or unique recipients | Whether temporary problems outlast message usefulness or queue policy |
| Policy and authentication rejection rate | Attempted messages by identity and provider | Sender configuration, alignment, reputation, or policy remediation |
| Unknown classification rate | All failure events | Parser coverage, evidence quality, and manual-review workload |
| Suppression additions by reason | Unique active recipients and stream | Whether automated actions match the actual failure mix |
| Complaint and unsubscribe rate | Delivered messages using the program definition | Consent, expectation, frequency, relevance, and preference design, kept separate from bounce handling |
Document numerator, denominator, deduplication rule, time window, timezone, and event source. “Bounce rate” is ambiguous when one team counts attempts, another counts recipients, and a third includes queue expirations and complaints.
Triage a sudden bounce spike without destroying evidence
- Confirm the signal. Check intake lag, duplicate events, parser changes, campaign volume, and denominator before treating the chart as a delivery incident.
- Contain the smallest affected scope. Pause or slow a provider, stream, tenant, identity, route, or template when evidence supports it. Avoid a global stop unless the failure is truly global.
- Preserve raw replies and queue state. Capture representative SMTP transcripts, DSNs, MTA logs, event payloads, timestamps, DNS, configuration, and recent changes.
- Segment the failure. Compare class, subject, detail, diagnostic text, SMTP phase, MX provider, source IP, domain, stream, template, and acquisition source.
- Find the first occurrence. The earliest event and the change immediately before it are usually more useful than the largest later batch.
- Test the leading cause. Repair one controlled scope and send only enough representative traffic to validate the path.
- Resume gradually. Watch live replies, queue age, provider concentration, complaints, and recurrence while increasing traffic.
- Reconcile state. Review automated suppressions created during the incident and reverse only those proven to be caused by a misclassification.
Do not mass-delete addresses because a provider rejected an unauthenticated stream, and do not repeatedly resend the same campaign because a provider deferred it. Both actions destroy the distinction between recipient quality and sender behavior.
Keep an auditable decision record
A useful event record can be compact while still preserving the decision path:
{
  "event_type": "delivery_failure",
  "action": "failed",
  "smtp_phase": "rcpt_to",
  "status": "5.1.1",
  "diagnostic": "[raw provider response retained separately]",
  "scope": "recipient",
  "classification": "invalid_recipient",
  "confidence": "high",
  "decision": "durable_address_suppression",
  "classifier_version": "2026-07",
  "occurred_at": "[UTC timestamp]"
}
For a provider-policy event, the scope and decision should instead identify the affected identity, provider, or stream and create a hold or investigation. The record should never pretend that a broad provider response proved the status of one mailbox.
Operational checklist for marketers and delivery teams
- Capture synchronous SMTP replies, asynchronous DSNs, queue expirations, complaints, and unsubscribes as distinct events.
- Retain the class, subject, detail, SMTP phase, action, diagnostic text, provider, route, message, stream, and attempt history.
- Use hard and soft only as reporting summaries, never as the sole suppression rule.
- Let the MTA retry transient delivery failures and prevent duplicate campaign resubmission.
- Map recipient, domain, provider, route, identity, stream, message, and infrastructure failures to separate scopes.
- Keep consent, unsubscribe, complaint, invalid-recipient, temporary-hold, and operational-hold states distinct.
- Make temporary holds expire or enter review; do not silently convert them into permanent suppression.
- Authenticate and deduplicate event intake, handle out-of-order delivery, and monitor parser failures.
- Keep the normalized classification and protected raw evidence with a versioned decision record.
- Analyze counts and rates by receiving provider, stream, identity, source, acquisition path, and time.
- Investigate sudden changes before applying bulk data actions.
- Repair acquisition, consent, correction, authentication, content, rate, routing, and infrastructure causes in the systems that own them.
- Run controlled recovery tests and review automated suppressions created during incidents.
Good bounce handling is not a bigger blocklist. It is a reliable decision system. Preserve the delivery evidence, classify the actual failure, act only at the proven scope, and keep every suppression or hold explainable. That protects sender reputation without sacrificing valid recipients to a misleading label.