Sender Reputation Monitoring: Signals That Deserve Action
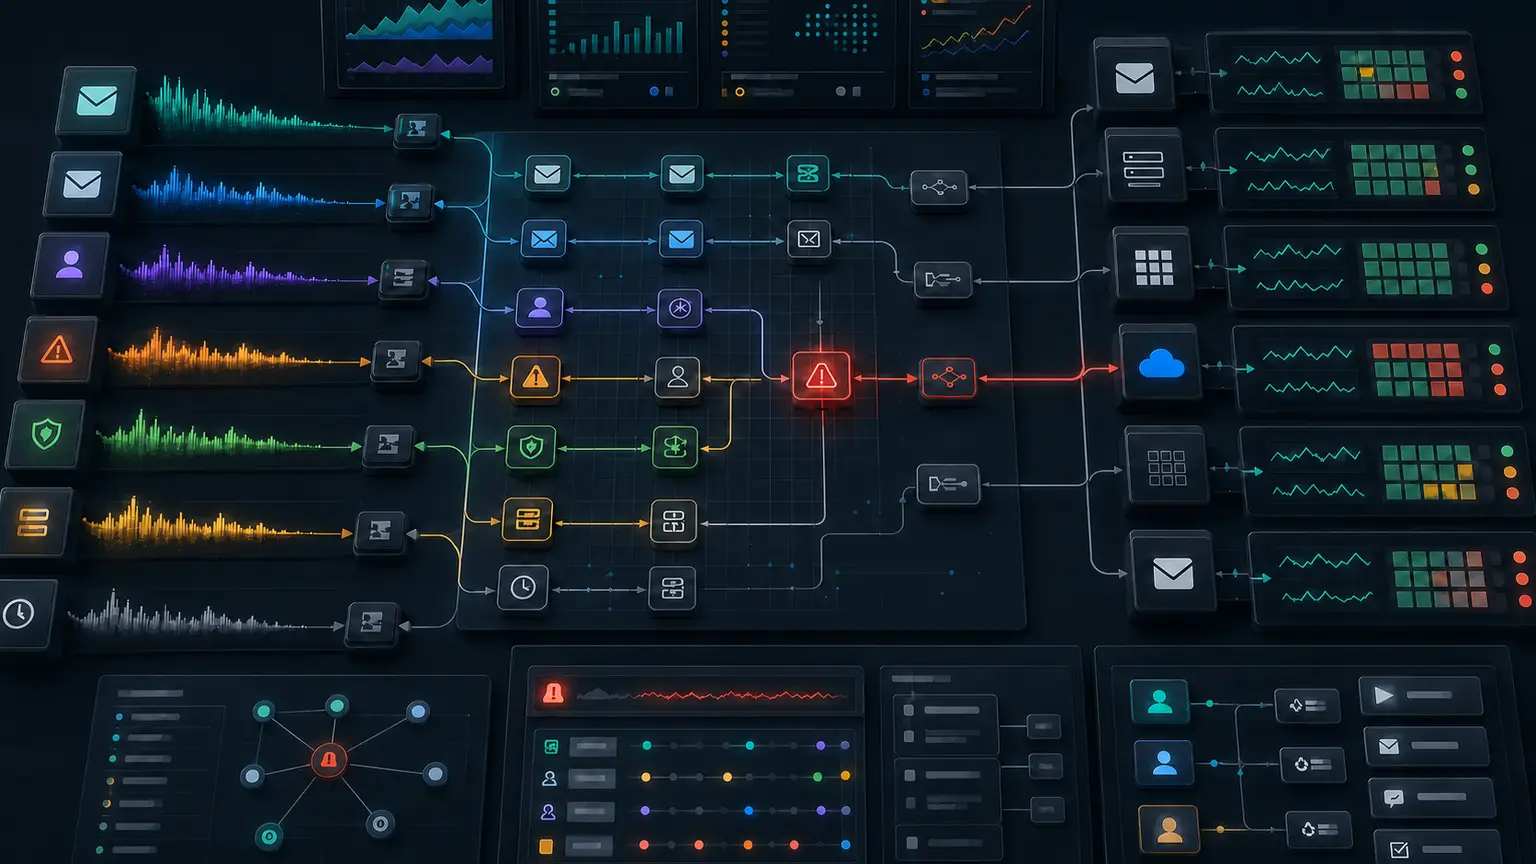
Sender reputation is not one score and it is not shared uniformly across mailbox providers. Receivers can evaluate the sending IP, authenticated domain, visible From identity, link domains, traffic stream, recipient cohort and recent behavior differently. A useful monitoring system therefore starts with an identity and traffic map, preserves recipient-level SMTP evidence, adds provider-native telemetry, and alerts only when the sample, persistence and operational context support a safe action.
Build a reputation model that matches the sending system
Start by inventorying every message stream and the identities a receiver can observe. At minimum, capture the RFC 5322 From domain, DKIM signing domain and selector, envelope or return-path domain, sending IP, PTR/HELO name, link and tracking domains, submission platform, tenant or business unit, and message class. Add the receiving organization because several recipient domains can share one mailbox platform.
Reputation symptoms should be attached to this graph. An IP problem may affect several domains on a shared route. A domain problem may follow traffic across IPs. A poor acquisition cohort can damage only one promotional stream while password resets remain healthy. Account-wide averages hide these distinctions.
Monitor the complete path, not a vendor score
| Boundary | Direct evidence | What it does not prove |
|---|---|---|
| Selection | Eligible, excluded and selected recipients with reason codes | That an SMTP attempt occurred |
| Transport | Connection result, full SMTP reply, accepted/deferred/rejected state | Final inbox or junk placement |
| Provider telemetry | Provider-specific complaint, reputation, authentication or error indicators | Every recipient outcome or every provider |
| Controlled placement | Observed folder for governed seed or panel accounts | Population-wide inbox percentage |
| Recipient response | Complaint, unsubscribe, qualified click, reply and conversion | Why a non-action occurred |
Keep these layers separate. A receiver can accept a message and place it in junk. A click can fall because tracking broke while reputation remains unchanged. Diagnosis begins at the earliest boundary that actually moved.
Use a signal catalog with an explicit owner
| Signal | Segment by | Likely owner | First evidence |
|---|---|---|---|
| User complaints | Provider, campaign, acquisition source, lifecycle | Audience and campaign | Complaint feed, campaign and consent record |
| Unknown users | Provider, list source, import, address age | Data acquisition | Complete 5xx response and source record |
| Temporary deferrals | Receiver, MX, IP, stream, response family | MTA/deliverability | 4xx text, queue age and rate change |
| Authentication drift | From, DKIM selector, return path, platform | DNS/platform | Received message and DMARC report |
| Domain/IP reputation | Provider, domain, IP and traffic class | Deliverability | Provider dashboard plus internal outcomes |
| Blocklist observation | Listing authority, IP/domain and scope | Security/deliverability | Authoritative listing record and logs |
| Placement movement | Provider, environment, sample method | Deliverability | Seed/panel provenance and SMTP acceptance |
Publish denominators and terminal timing
attempted recipients = recipients with at least one SMTP attempt
accepted recipients  = recipients receiving final SMTP acceptance
complaint rate       = complaints / the documented provider or program denominator
unknown-user rate    = terminal unknown-user recipients / attempted recipients
deferral incidence   = recipients receiving matching 4xx / attempted recipients
queue-age p95        = 95th percentile age of unresolved queued recipients
Retries remain attached to the same recipient; they are not new recipients. State the cutoff because a deferred recipient can later become accepted or expire. Provider complaint dashboards may use a different denominator from the ESP, so label them separately rather than forcing them to match.
Always retain absolute counts. A move from one complaint to three is a 200% increase but may not justify the same response as a move from 1,000 to 3,000.
Use Gmail Postmaster Tools with its documented limits
Gmail Postmaster Tools exposes compliance status, user-reported spam, IP and domain reputation, feedback loop identifiers, authentication, encryption and delivery errors for personal Gmail traffic. Google states that the data is not real time and that low-volume days can be omitted for privacy. The Compliance dashboard is primary-domain oriented even though subdomain traffic contributes to classification.
Google recommends keeping the Postmaster user-reported spam rate below 0.10% and avoiding 0.30% or higher. Treat 0.10% as a warning boundary, not an operating target. The displayed spam rate can appear deceptively low when much traffic already goes to spam because fewer inbox recipients can report it. Correlate it with the Feedback-ID campaign view, SMTP outcomes, audience changes and business response.
Operate Yahoo and AOL monitoring by campaign and complaint source
Use Yahoo Sender Hub guidance, the complaint feedback loop, complete SMTP replies and internal campaign evidence together. Yahoo publishes a maximum spam complaint rate of 0.3% for bulk senders, but a mature program should operate materially below that boundary. Register every eligible DKIM domain, route reports into durable suppression and retain the campaign, acquisition source and consent evidence that explain each complaint.
Group Yahoo-hosted domains by receiving organization while preserving the original recipient domain for investigation. Rate-limit and error behavior can change over time, so classify complete response text and keep an unknown category. Do not hard-code one connection or message limit as a permanent provider promise.
Use Microsoft SNDS and JMRP as IP and complaint evidence
Microsoft SNDS provides data about IPs for which the operator can prove responsibility, and the Junk Email Reporting Program supplies user junk reports. SNDS can help detect unusual sending, compromised infrastructure and reputation changes, but it does not replace recipient-level Outlook SMTP evidence or domain-level analysis.
Microsoft moved SNDS to its newer portal in 2026 and announced that trap hit counts would no longer be included from July 22, 2026. Do not build a current alert that expects exact SNDS trap counts. Preserve the SNDS color/status, complaint samples, IP volume and complete 4xx/5xx responses, then correlate them with the From/DKIM domains and streams using that IP.
Treat DMARC aggregate reports as an identity inventory
DMARC aggregate reports show which sources claim a domain, how SPF and DKIM evaluated, whether identifiers aligned, and what disposition the receiver reported. In May 2026, RFC 9990 standardized DMARC aggregate reporting and obsoleted the aggregate-reporting portions of RFC 7489. Store the original compressed/XML report, checksum, report ID, date range, parser version and normalized rows.
Alert on a new material source, a new selector, aligned-pass decline, sudden volume shift or unexpected disposition. A source IP alone is not authorization: map it to a contracted platform, business purpose, accountable owner and expected aligned domain. Keep forwarding and intermediary effects visible rather than classifying every alignment failure as spoofing.
Use blocklists as scoped observations
A blocklist entry has meaning only for receivers that query or use that list and for the listed IP or domain. Monitor authoritative listing sources relevant to the infrastructure, record the first-seen time, listing category and affected traffic, and correlate with actual SMTP replies. Avoid dashboards that transform hundreds of obscure lists into one alarming score.
Before requesting delisting, stop the cause: compromise, open relay, unsafe acquisition, trap-prone data or uncontrolled tenant traffic. Save evidence of remediation and follow the operator’s official process. Rotating infrastructure to avoid a listing spreads risk and leaves the failure unresolved.
Create baselines by receiver, stream and volume band
Use comparable weekdays, campaign types and volume bands. Capture median and a robust spread such as median absolute deviation, then require a minimum denominator and persistence window. Seasonality, a new product release and billing cycles can change expected traffic without indicating reputation damage.
candidate_alert =
  sample_size >= minimum_sample
  AND current_rate > absolute_guardrail
  AND deviation_from_baseline >= sensitivity
  AND condition_persists_for >= evaluation_window
Use absolute policy boundaries where a provider publishes them, and learned baselines for local operational signals. Do not allow the baseline to normalize a chronically harmful complaint or invalid-recipient rate.
Design alerts that start an investigation
| Alert | Required context | First safe action |
|---|---|---|
| Complaint guardrail | Provider, stream, source, count, denominator, campaigns | Pause the implicated cohort or campaign |
| Deferral surge | MX, response family, IP, queue age, recent rate | Reduce that receiver key and preserve replies |
| Authentication drop | From, DKIM selector, return path, platform/deployment | Stop affected route and inspect received artifact |
| Unknown-source DMARC volume | IP/ASN, authentication domains, owner search | Confirm authorization before changing policy |
| Reputation category decline | Provider, domain/IP, volume, complaints, recent changes | Investigate; do not rotate identity automatically |
| Oldest queue breach | Receiver, message class, attempts, expiry and disk | Protect critical stream and stop new bulk injection |
Every page should link to the exact dashboard slice, log query, DNS evidence, campaign and runbook. “Reputation decreased” without scope sends the operator back to the beginning.
Create recipient-level evidence queries
SELECT receiver_org, stream, smtp_class,
       COUNT(DISTINCT recipient_id) AS recipients,
       MAX(queue_age_seconds) AS oldest
FROM delivery_attempts
WHERE event_time >= :window_start
GROUP BY receiver_org, stream, smtp_class;

SELECT acquisition_source, campaign_id,
       COUNT(DISTINCT complaint_recipient) AS complaints,
       COUNT(DISTINCT accepted_recipient) AS accepted
FROM campaign_outcomes
WHERE provider = :provider
GROUP BY acquisition_source, campaign_id;
Adapt names to the actual schema and protect recipient data. The first query identifies where transport changed; the second connects complaints to acquisition and campaign decisions. Keep full SMTP replies in a related evidence table rather than only a simplified status label.
Put changes and signals on one timeline
- Audience import, segment rule and consent-form releases.
- Campaign launches, resend behavior and volume ramps.
- ESP, IP pool, MTA route or throttling changes.
- DKIM selector, return path, DNS, PTR, TLS and link-domain changes.
- Template, redirect, attachment and unsubscribe changes.
- Provider telemetry, complaint, deferral, rejection and queue movements.
Record deployment time in UTC and the first affected message. Provider dashboards can lag, so correlate the observation date with internal event time rather than assuming they move simultaneously. Change one variable during recovery whenever possible.
Scenario: complaint rate rises after audience expansion
A promotional stream adds a reactivated cohort from an older acquisition source. Gmail acceptance remains stable, but Postmaster spam rate and Feedback-ID complaints rise the next day. The domain reputation category later weakens. An account-wide dashboard looks normal because transactional volume dominates.
The operator segments by stream and campaign, pauses the reactivated cohort, verifies suppression and consent evidence, and keeps the stable active cohort unchanged. The team repairs the eligibility rule, adds a bounded re-engagement path and resumes only after complaint evidence remains below the recovery threshold for the defined window. It does not move the domain or IP.
Scenario: provider deferrals create a queue backlog
One receiving organization begins returning rate-related 4xx responses to a single sending IP after a burst. Queue count grows, but the more important signal is oldest age. Other providers and the transactional stream remain healthy. Repeated immediate retries would increase pressure.
The operator reduces concurrency and message rate only for that receiver/IP/stream key, applies exponential backoff with jitter, pauses new promotional injection and protects fresh transactional traffic. Recovery uses small probes and gradual queue drain. Full response text and acceptance windows prove recovery; a global reputation score is not used as the decision.
Use a boundary-first reputation incident runbook
- Scope: identify provider, stream, domain, IP, cohort and first affected time.
- Preserve: save SMTP replies, received headers, queue samples, provider views and recent releases.
- Contain: pause the narrow unsafe cohort or receiver route while keeping healthy critical traffic isolated.
- Classify: decide whether the earliest failure is selection, authentication, transport, complaint, placement or measurement.
- Correct: make one reversible change and test controlled recipients.
- Recover: ramp under explicit acceptance, complaint, queue and provider thresholds.
- Review: fix the missing control and retain the incident timeline.
Do not request provider mitigation before meeting published authentication, unsubscribe and complaint requirements.
Run daily operations and a weekly decision review
Daily automation should check data freshness, queues, receiver-specific response changes, authentication, complaint feeds, Postmaster/SNDS availability and material DMARC sources. The weekly review should focus on changed baselines, unresolved sources, risky upcoming sends, recent acquisition quality, alert usefulness and open incident actions.
Remove alerts that never change a decision, but retain safety guardrails. Assign every action an owner and due date. If the meeting only reads dashboard colors, the monitoring system is not yet operational.
Sender reputation monitoring checklist
- Map every From, DKIM, return-path, link, IP, PTR, stream and receiver.
- Keep selection, transport, provider, placement and business evidence separate.
- Count unique recipients and publish every denominator.
- Retain complete SMTP replies and unresolved queue age.
- Use Gmail, Yahoo and Microsoft native tools within their documented scope.
- Normalize current DMARC aggregate reports and map sources to owners.
- Alert only with minimum samples, persistence and actionable context.
- Correlate changes, campaigns and provider signals on one UTC timeline.
- Contain the narrow unsafe path; do not rotate identities reflexively.
- Validate recovery with independent signals and gradual traffic.
Primary references
- Google email sender guidelines
- Google Postmaster Tools dashboards
- Google Feedback Loop
- Yahoo Sender Hub best practices
- Yahoo complaint feedback loop
- Microsoft Smart Network Data Services
- RFC 9990: DMARC Aggregate Reporting
- RFC 5321: SMTP
- RFC 3463: Enhanced Mail Status Codes