Microsoft Outlook High-Volume Sender Requirements: Enforcement Guide
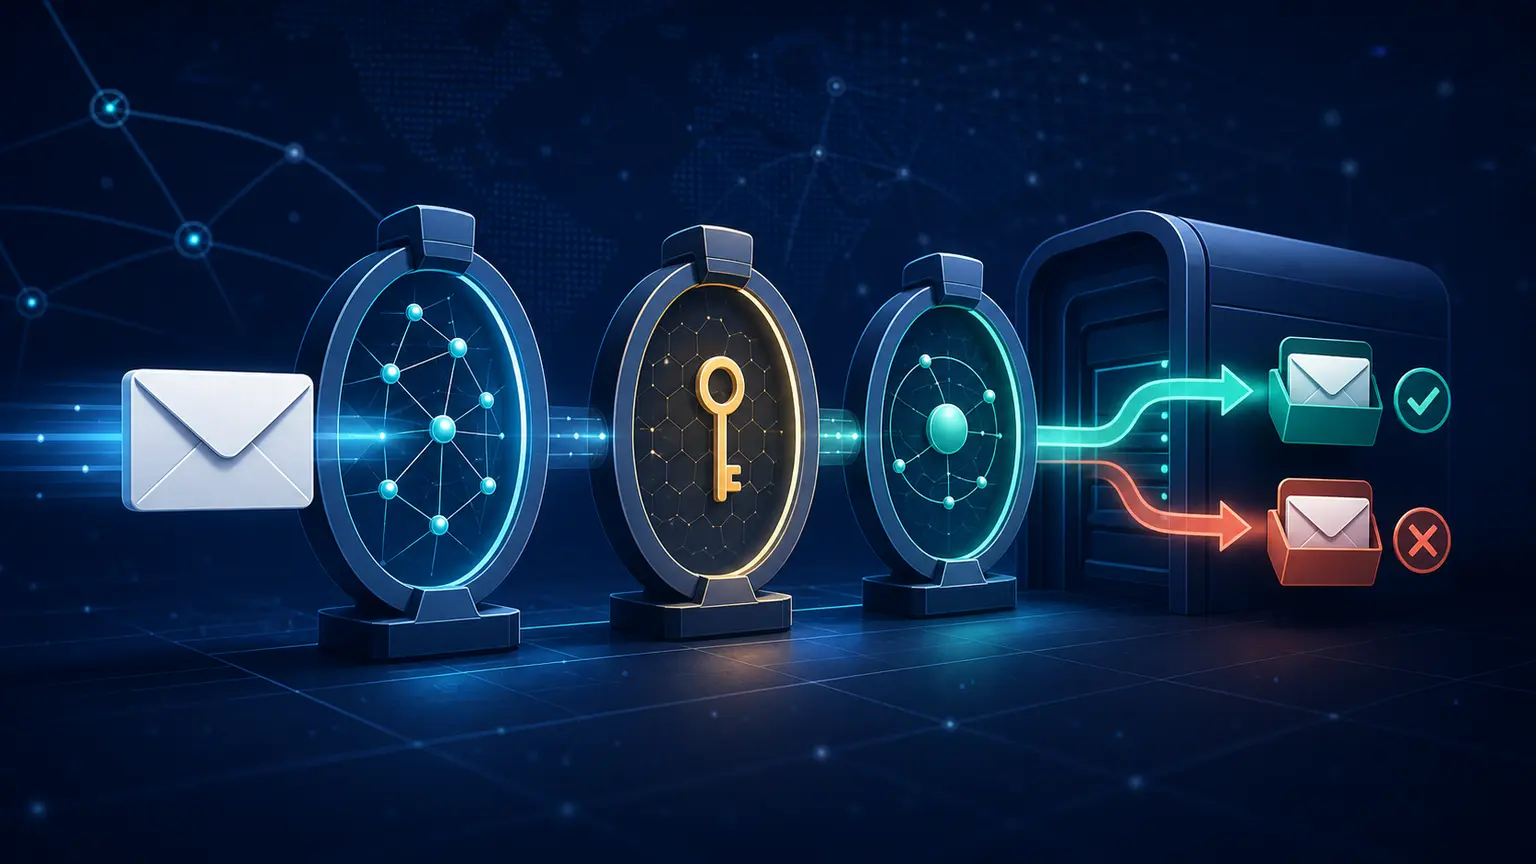
Microsoft now enforces stronger authentication for domains sending more than 5,000 messages per day to Outlook.com consumer accounts. SPF must pass, DKIM must pass, and DMARC must be published with at least p=none and pass through an aligned SPF or DKIM identity. A high-volume message that does not meet the required authentication level can be rejected with 550 5.7.515.
This is no longer a future policy announcement. The enforcement date was May 5, 2025. A production response therefore needs more than three DNS checks. Senders must identify every visible From domain in scope, validate every primary and failover route, preserve the SMTP evidence, separate authentication failures from reputation problems, and give each customer domain an owner.
The enforcement is active, not a future warning
Microsoft announced the requirements in April 2025 and updated the enforcement language before the May deadline. The current Microsoft high-volume sender announcement says that non-compliant messages can be rejected with this response:
550 5.7.515 Access denied, sending domain [SendingDomain]
does not meet the required authentication level.
Microsoft’s Outlook.com troubleshooting page now documents that code as a permanent policy rejection for high-volume sender authentication. Some Microsoft pages still contain older language about junk-folder placement before rejection. Operators should plan for the permanent failure that the active SMTP documentation and real delivery responses expose, not for a grace period.
Authentication compliance is an acceptance requirement, not an inbox guarantee. A message can pass SPF, DKIM, and DMARC and still be throttled, filtered, junked, or blocked because of IP reputation, domain reputation, complaints, recipient quality, content, URLs, traffic changes, or other policy signals.
Know exactly which Microsoft service is in scope
The announcement applies to the Outlook.com consumer service. Microsoft explicitly names consumer addresses hosted under Outlook.com, Hotmail, and Live, while its sender-support material also covers MSN addresses. It is not a blanket statement that every Exchange Online tenant applies the same consumer high-volume rule in the same way.
| Destination | How to treat it | Operational evidence |
|---|---|---|
| Outlook.com consumer mailbox | In scope for the high-volume sender rule | Recipient domain, Microsoft consumer MX, SMTP response, and received headers |
| Hotmail, Live, or MSN consumer mailbox | Manage through the same Outlook.com sender policy path | Actual MX and SMTP peer, not only the address suffix |
| Microsoft 365 or Exchange Online business tenant | Do not assume the consumer threshold is the tenant policy | Tenant MX, recipient organization, tenant controls, and returned SMTP diagnostics |
| Custom domain routed through Microsoft infrastructure | Classify from current DNS and the connection actually used | MX snapshot, resolved peer, timestamp, and delivery response |
A static list of dozens of regional Hotmail or Live suffixes becomes stale and still misses custom domains. Record the envelope recipient domain, resolved MX, destination provider classification, and SMTP peer at send time. That evidence shows where the platform attempted delivery even if hosting changes later.
Treat 5,000 messages as an operational boundary
Microsoft’s current sender policies describe the scope as domains sending more than 5,000 messages per day to Outlook.com accounts. The public material does not fully define every counting edge case, including the exact daily reset window, organizational-domain rollup, subdomain inheritance, or how long high-volume classification persists.
Do not build a compliance program around staying one message below the threshold. Authenticate every legitimate stream, and treat any domain that approaches the boundary as in scope. For a multi-customer platform, keep at least these daily dimensions:
- RFC 5322 visible From domain and its organizational domain;
- envelope Mail From domain;
- DKIM
d=domains and selectors; - messages attempted and accepted for Microsoft consumer destinations;
- SPF, DKIM, and DMARC results observed on received samples;
- route, sending IP, pool, region, MTA, ESP, and failover path;
- temporary and permanent SMTP responses by exact enhanced status code.
An internal alert below 5,000 gives the team time to fix a new route or customer domain before the boundary is crossed. That alert is an operating margin, not a Microsoft-published threshold.
Make SPF pass on every sending route
SPF authorizes the SMTP client through the envelope Mail From domain, or the HELO identity when the envelope sender is empty. Microsoft requires SPF to pass for high-volume senders. A valid-looking TXT record is not enough if the connecting IP is absent, an include chain fails, or a fallback route uses a different envelope domain.
Review the complete authorization path described by RFC 7208:
- publish one SPF record for each domain that can appear as the envelope sender;
- authorize every current primary, regional, disaster-recovery, and third-party source;
- remove retired senders rather than accumulating permanent includes;
- keep the evaluation within the SPF DNS-lookup limit;
- use a controlled HELO name with valid forward and reverse DNS;
- test the IP that actually connected to Microsoft, not only the planned route.
SPF passing on the provider’s shared bounce domain can satisfy the independent SPF check, but it passes DMARC through SPF only when the authenticated Mail From domain aligns with the visible From domain. An aligned DKIM signature can provide the DMARC path when SPF is valid but not aligned.
Make DKIM pass after final message assembly
Microsoft also requires DKIM to pass. Sign with a domain the sender controls or has explicitly delegated, publish the correct selector, and apply the signature after the final header and body transformations. A third-party ESP does not remove the customer’s responsibility to configure the required DNS delegation and verify the received result.
A production DKIM review should confirm:
- the selector resolves publicly from more than one resolver;
- the public key matches the active private key;
- the signing domain is intentional for that customer and stream;
- the message is not modified after signing in a way that breaks the signature;
- all regions, templates, MTAs, API paths, and failover routes sign correctly;
- key rotation overlaps safely and retired keys are removed only after queued mail clears.
RFC 6376 defines DKIM verification. The evidence that matters is the received message and its trusted Authentication-Results, not the mere presence of a DKIM-Signature field in a pre-send preview.
Make DMARC pass through an aligned identity
Microsoft requires a DMARC record with at least p=none. A monitoring policy satisfies the minimum published policy level, while p=quarantine and p=reject are stronger enforcement choices that should follow a controlled rollout.
DMARC must also pass. That requires the visible RFC 5322 From domain to align with at least one authenticated identity:
- SPF path: SPF passes and the envelope Mail From domain aligns with the visible From domain;
- DKIM path: DKIM passes and the signature’s
d=domain aligns with the visible From domain.
Microsoft still requires the separate SPF and DKIM checks to pass. DMARC passing through DKIM does not excuse an SPF failure, and DMARC passing through SPF does not excuse a DKIM failure.
An illustrative DNS design might look like this:
bounce.news.example. IN TXT "v=spf1 ip4:192.0.2.10 -all"
s2026._domainkey.news.example. IN TXT "v=DKIM1; k=rsa; p=PUBLIC_KEY"
_dmarc.news.example. IN TXT "v=DMARC1; p=none; rua=mailto:[email protected]"
The domains and IP above are reserved for documentation. The public key is a placeholder. A real rollout needs a valid key, an operational aggregate-report mailbox, and an inventory showing that every legitimate source can pass before policy enforcement is increased. The full diagnostic method is covered in the SPF, DKIM, and DMARC troubleshooting guide.
Read the three checks together
| SPF | DKIM | DMARC | Microsoft high-volume outcome |
|---|---|---|---|
| Pass | Pass | Pass through aligned SPF, DKIM, or both | Meets the published authentication combination. Reputation and other policy checks still apply. |
| Fail | Pass and aligned | Pass through DKIM | Not compliant because Microsoft requires SPF to pass separately. |
| Pass and aligned | Fail | Pass through SPF | Not compliant because Microsoft requires DKIM to pass separately. |
| Pass | Pass | Fail because neither identity aligns | Not compliant because DMARC does not pass. |
| Pass | Pass | No DMARC record | Not compliant because a policy of at least p=none is required. |
| Pass | Pass | Pass | Authentication compliant, but not guaranteed acceptance or inbox placement. |
Store the three results separately. A single Boolean named authenticated hides which protocol failed, whether alignment passed, and whether the route meets Microsoft’s stricter combination.
Do not turn From and Reply-To recommendations into invented prohibitions
Microsoft's high-volume authentication rule does not prohibit local parts such as noreply@, admin@, postmaster@, or marketing@. Do not invent such a prohibition.
The announcement instead recommends a valid primary sender identity: the From or Reply-To address should reflect the real sending domain and provide a usable reply path. The practical controls are legitimacy, routing, monitoring, and recipient experience, not the spelling before the @.
| Identity choice | Safe interpretation | Risk to avoid |
|---|---|---|
[email protected] | Not automatically prohibited. Provide a monitored Reply-To or another clear support path when a response is expected. | A dead address combined with no unsubscribe, help, or response channel |
[email protected] | Appropriate when it reaches the actual support workflow | A decorative address that silently discards replies |
[email protected] | Appropriate when it honestly describes the stream and domain | A misleading display name or unrelated From domain |
| Customer-specific From domain | Best when the customer controls it and the platform can authenticate it on every route | Sending before DNS delegation and DKIM validation are complete |
Keep the visible From, envelope Mail From, Reply-To, DKIM domain, and support destination as separate fields in the sender-identity inventory. They perform different protocol and business functions.
Keep unsubscribe requirements in the correct category
Microsoft’s 2025 announcement recommends a functional, clearly visible unsubscribe path for marketing and bulk mail. The broader Outlook.com policies say the unsubscribe mechanism must be clearly documented and easy to find. The announcement does not make RFC 8058 one-click unsubscribe part of the three high-volume authentication checks.
That distinction is not a reason to omit one-click unsubscribe. Marketing programs often send to Gmail, Yahoo, and Microsoft recipients in the same campaign. Gmail requires RFC 8058 one-click unsubscribe for high-volume marketing and subscribed mail, and Yahoo requires a functioning List-Unsubscribe mechanism for bulk promotional mail. A cross-provider implementation should therefore support:
List-Unsubscribe: <https://unsubscribe.example/u/opaque-token>
List-Unsubscribe-Post: List-Unsubscribe=One-Click
Keep the token opaque, process the POST without requiring a login, protect the endpoint against abuse, and also include a visible body link. Do not present one-click unsubscribe as the fix for 550 5.7.515; that code points to authentication.
Compare Microsoft, Gmail, and Yahoo without merging the rules
Microsoft, Gmail, and Yahoo have overlapping but non-interchangeable requirements. Compare each provider against its own current first-party documentation:
| Control | Microsoft consumer | Gmail personal | Yahoo-hosted consumer mail |
|---|---|---|---|
| High-volume scope | Domains sending more than 5,000 messages per day to Outlook.com accounts | Close to 5,000 or more in 24 hours, aggregated by primary domain; status persists once assigned | Significant volume; Yahoo does not publish a numeric threshold |
| SPF and DKIM | Both must pass | Both required for bulk senders | Both required for bulk senders |
| DMARC | At least p=none; DMARC must pass through aligned SPF or DKIM | At least p=none; direct mail must align through SPF or DKIM | At least p=none; DMARC must pass with aligned SPF or DKIM |
| Unsubscribe | Easy, clearly documented unsubscribe is required by general policy; the 2025 authentication rule does not specify RFC 8058 | One-click plus a visible body link for marketing and subscribed messages; honor within 48 hours | List-Unsubscribe for marketing and subscribed messages, a visible body link, and completion within two days |
| Published complaint ceiling | No numeric ceiling in the high-volume authentication announcement | Keep Postmaster Tools spam rate below 0.30% | Keep spam complaint rate below 0.3% |
| Authentication enforcement | 550 5.7.515 permanent rejection can identify the required-authentication failure | Temporary or permanent failures and spam placement can apply | Spam placement or rejection can apply, with provider-specific SMTP codes |
Meet each provider’s own rule rather than reducing all three to a single “bulk sender compliant” flag. A platform may be compliant for Microsoft authentication while failing Gmail TLS or unsubscribe requirements, or it may satisfy Gmail while a Microsoft route has a broken SPF include.
Build controls for thousands of customer domains
A multi-tenant platform cannot manage this policy with a spreadsheet reviewed after a rejection. Create a sender-domain registry before allowing production volume. Each customer and visible From domain should map to:
| Control record | Purpose | Release gate |
|---|---|---|
| Customer and From domain | Assign ownership and calculate volume | Verified control of the domain |
| Envelope domain and SPF sources | Authorize every connecting IP and ESP | SPF passes on primary and failover routes |
| DKIM domain, selector, and key owner | Prove the signing path and support rotation | Received-message DKIM pass |
| DMARC policy and alignment path | Connect the visible From domain to authenticated identities | DMARC record present and received-message pass |
| Destination-provider volume | Identify domains approaching Microsoft’s boundary | Alert before the internal safety threshold |
| Route inventory | Cover region, pool, MTA, ESP, and disaster recovery | Every route has a recent passing sample |
| SMTP and complaint evidence | Separate authentication, reputation, and recipient failures | Events reach the central ledger with exact codes |
Do not expose customer, campaign, or recipient identifiers in authentication headers. Use an opaque Message-ID connected to a private send ledger, as described in the Message-ID implementation guide. That mapping lets a trusted rejection or complaint resolve to the responsible customer, route, and message without publishing internal keys.
Validate the received message and DNS state
DNS inspection shows what is published now. A received sample shows what Microsoft evaluated for one real message. Use both.
dig +short TXT bounce.news.example
dig +short TXT s2026._domainkey.news.example
dig +short TXT _dmarc.news.example
dig +short -x 192.0.2.10
Then send a controlled message through the exact production route to an Outlook.com consumer mailbox and inspect the raw source. Confirm:
- the visible From, Return-Path, and DKIM
d=identities are the intended values; - SPF, DKIM, and DMARC each show the expected result at a trusted receiving boundary;
- the DMARC result identifies the aligned identity used for the pass;
- the connecting IP, HELO name, reverse DNS, and forward DNS are coherent;
- the DKIM signature survives link tracking, footer insertion, encoding, and relay processing;
- the same Message-ID and internal record connect the received message to the route and customer.
Repeat the test for each message stream, region, selector, sending platform, and failover path. One passing sample from the primary route does not validate the disaster-recovery route.
Handle 550 5.7.515 as a domain authentication rejection
A 550 response is permanent for that delivery attempt. Microsoft’s general sender policy says a sender must not retransmit the same message to the same recipient after a 5xx response. Do not leave the message in a rapid retry loop.
At the same time, do not automatically suppress the recipient as invalid. The mailbox may be perfectly valid. The rejection reports that the sending domain failed Microsoft’s authentication requirement.
- Preserve the complete SMTP response, enhanced code, timestamp, peer, queue ID, customer, route, and Message-ID.
- Read the
Spf=,Dkim=, andDMARC=details when Microsoft includes them. - Identify the visible From domain and the exact route that produced the message.
- Compare a rejected message with a known-good received sample from the same customer and stream.
- Fix the failed DNS, signing, alignment, or routing control.
- Send a new controlled test message after the correction. Do not replay the original rejected queue item as if the 5xx were temporary.
The bounce-handling system should classify this as a sender-domain authentication failure, not an unknown-user hard bounce. The bounce handling guide explains why suppression scope must follow the evidence.
Separate authentication failure from reputation and rate limits
| Response family | Primary meaning | First investigation |
|---|---|---|
550 5.7.515 | High-volume sending domain does not meet the required authentication level | SPF, DKIM, DMARC, alignment, and the exact route |
421 RP-001, RP-002, or RP-003 | Temporary rate or connection limit associated with IP or domain reputation | Traffic change, concurrency, IP reputation, complaints, and retry pacing |
550 SC-001 | Permanent policy rejection that can involve content or IP/domain reputation | Full response, content and URL changes, reputation, and incident history |
550 SC-004 | Complaint-related IP block | JMRP complaints, list source, consent, frequency, and affected IP |
550 DY-001 or DY-002 | Dynamic IP or compromised-system concern | Network ownership, host security, queue abuse, and outbound sources |
Do not respond to every Microsoft deferral by changing DNS, and do not respond to an authentication rejection by slowing the queue. The exact SMTP code determines the first branch of the investigation.
Use SNDS and JMRP for the evidence they actually provide
Smart Network Data Services provides Microsoft’s view of the health and reputation of sending IP space. The Junk Email Reporting Program provides complaint reports when Outlook.com users mark messages as junk or phishing. These services help with reputation, abuse detection, and complaint processing, but they do not replace direct SPF, DKIM, and DMARC validation.
The SNDS portal changed in July 2026. Microsoft’s current announcement says the new portal replaces the former sender-support URL, automated access links must be updated, and trap-hit counts were removed from the Data Report starting July 22, 2026. Do not build a compliance control that depends on an old SNDS URL or on trap-hit counts continuing to appear.
For a multi-customer platform:
- keep network ownership and access authorization current for every sending range;
- connect JMRP complaint evidence to the correct recipient-delivery record and customer;
- monitor unexpected volume, complaint movement, and reputation changes by IP;
- keep domain authentication monitoring separate from IP-reputation monitoring;
- treat missing SNDS data as missing visibility, not proof that reputation is good.
Test every route before and after changes
A safe release test covers more than the default campaign path:
| Test case | What it can expose |
|---|---|
| Primary marketing route | Normal SPF, DKIM, DMARC, unsubscribe, and reputation behavior |
| Transactional route | A separate From domain, selector, envelope domain, or signing service |
| Regional route | Missing SPF authorization, selector replication, or different body transformation |
| Disaster-recovery route | Configuration drift that remains hidden until an incident |
| New DKIM selector | DNS propagation, incorrect key pairing, or premature old-key removal |
| ESP migration or split traffic | One provider passing while the other fails alignment or signing |
| Forwarded message | SPF failure after forwarding while an intact aligned DKIM signature preserves DMARC |
Keep a small seed set for direct raw-source inspection, but do not interpret a seed inbox result as a population-wide placement rate. The purpose here is protocol and route validation.
Run a focused incident response
- Confirm the scope: identify affected customer domains, Microsoft consumer destinations, streams, regions, routes, and start time.
- Preserve evidence: save complete SMTP replies, DNS snapshots, signed raw messages, queue IDs, Message-IDs, deployment events, and route changes.
- Separate failures: group
5.7.515authentication rejections apart fromRP,SC, recipient, and network responses. - Find the failed control: determine whether SPF, DKIM, DMARC publication, alignment, or a particular sending route is responsible.
- Limit impact: pause or reroute only the affected domain and stream when a known-good authenticated path exists. Do not move traffic onto an untested shared pool.
- Correct safely: apply the narrow DNS, signer, envelope, or routing fix and allow for propagation where relevant.
- Validate: send a new controlled message, inspect the received source, and watch the exact SMTP response distribution.
- Close the gap: update the sender registry, tests, alerts, runbook, and ownership so the same route cannot drift silently.
Contact Microsoft sender support only after the published requirements have been checked and the evidence is ready. A support request is not a substitute for a passing authentication path, and submitting one does not guarantee delivery.
Use this production checklist
- Inventory every visible From domain and its Microsoft consumer volume.
- Authenticate every primary, regional, third-party, and failover route before production use.
- Require SPF pass and DKIM pass independently.
- Publish DMARC with at least
p=noneand confirm DMARC passes through an aligned SPF or DKIM identity. - Verify From, Reply-To, envelope Mail From, DKIM, and support identities as separate controlled fields.
- Provide an easy unsubscribe path and support provider-specific one-click requirements for marketing mail.
- Capture exact SMTP codes and classify
550 5.7.515as sender-domain authentication failure. - Do not suppress a valid recipient merely because the sender domain failed authentication.
- Use SNDS for IP-reputation evidence and JMRP for complaint processing, not as substitutes for authentication tests.
- Repeat received-message validation after DNS, signer, MTA, ESP, routing, region, or failover changes.
Microsoft’s high-volume rule is straightforward at the protocol level and demanding at platform scale. Every route must make SPF pass, DKIM pass, and DMARC pass for every in-scope customer domain. NitWings can help with authentication and transport security, multi-tenant sender controls, Microsoft rejection analysis, and production validation across MTAs and ESPs.