ESP vs SMTP Relay: Architecture, Responsibility and Selection
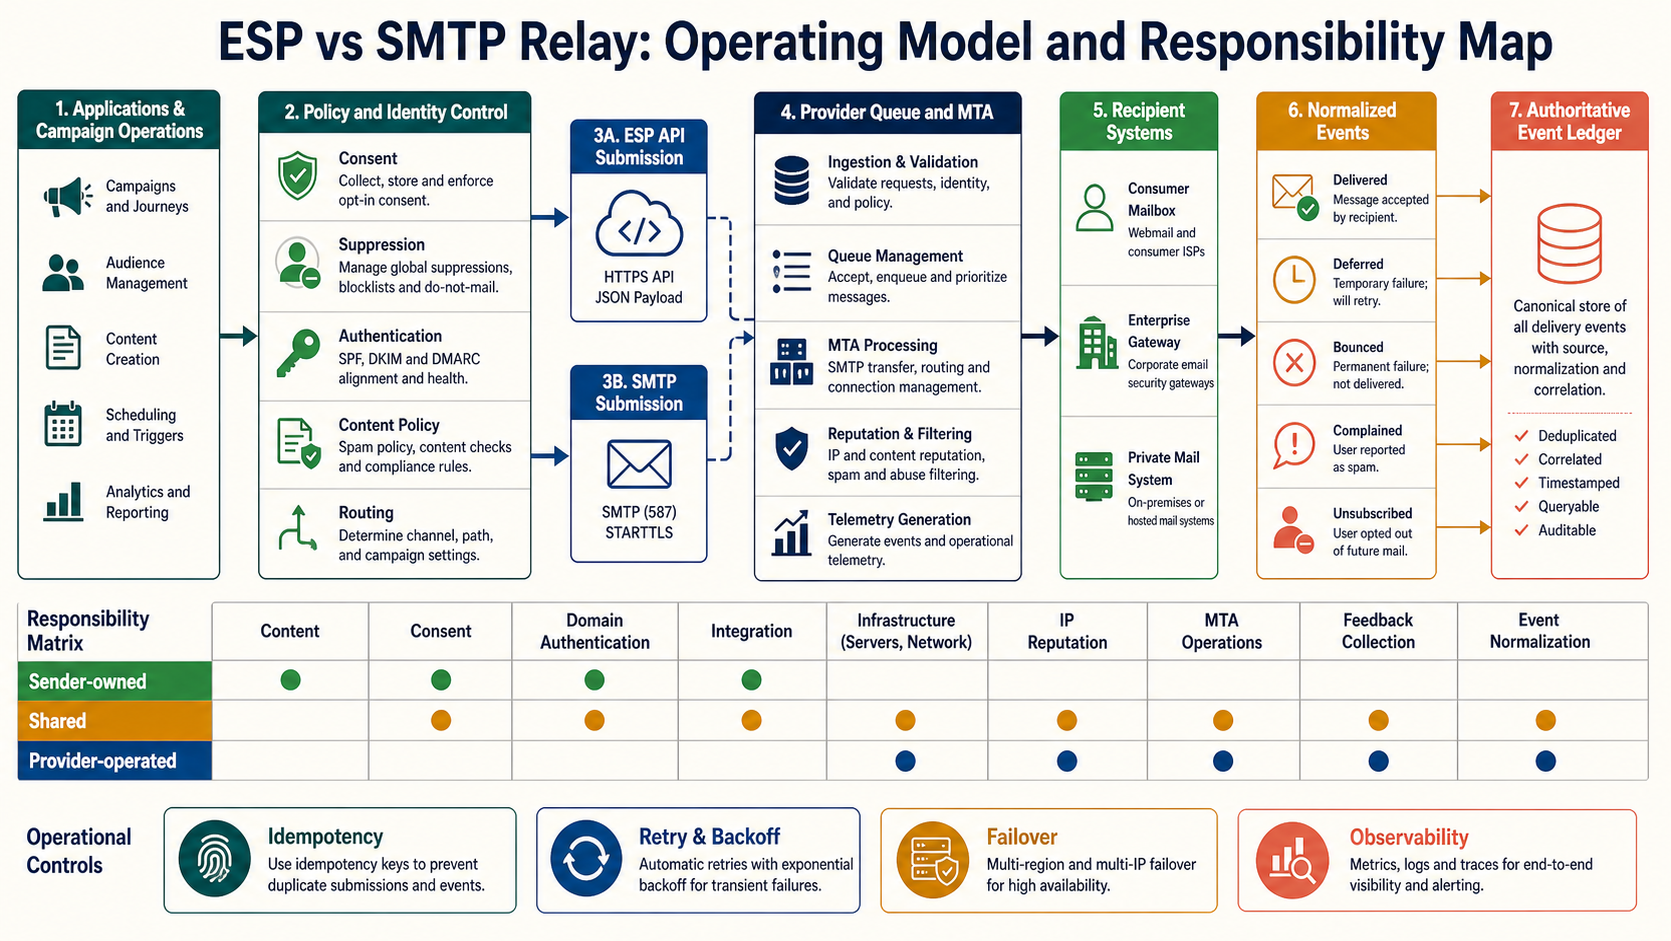
An ESP and an SMTP relay are not mutually exclusive labels. SMTP is the transfer protocol; a relay service may provide transport APIs, queues and feedback, while an email service provider can add audience management, templates, campaigns, automation, preferences and analytics. Products often span both. Selection should begin with message types, integration, ownership and failure requirements, then map each responsibility instead of assuming the platform handles deliverability.
Define the operating decision before choosing tactics
Choose an architecture and provider responsibility model that safely produces, transmits, observes and governs each email stream under the organization scale, security and recovery requirements.
For ESP vs SMTP Relay, write the eligible population, excluded population, decision owner, effective time, expiry and expected recipient benefit before selecting software or creative. This prevents a dashboard metric from becoming the goal and gives reviewers a concrete standard for rejecting unsafe or irrelevant execution.
Separate adjacent problems that need different controls
| In scope | Separate decision | Why separation matters |
|---|---|---|
| SMTP protocol | Relay product | A protocol is not a complete service |
| ESP interface | Transport path | Campaign UI may use several relays |
| Delivery | Inbox placement | Receiver acceptance does not guarantee inbox |
| Vendor feature | Customer responsibility | Authentication and permission remain shared work |
| Marketing stream | Transactional stream | Purpose, latency and suppression differ |
Within ESP vs SMTP Relay, a clean boundary keeps one favorable signal from overriding a harder requirement. Permission, suppression, identity, product state, provider acceptance and business outcome remain distinct even when one platform displays them together.
Choose the correct identity and decision unit
The primary ESP vs SMTP Relay decision unit is a message stream and sending identity mapped to an application, provider route and accountable operating team. Define when person, address, account, household, device, order, campaign and receiving-provider state may be joined. Record the join source, confidence, effective time and collision behavior. A shared mailbox, forwarded message or security scanner must not silently become evidence about one individual.
Minimize downstream data for ESP vs SMTP Relay. Rendering and dispatch systems usually need the selected treatment and reason code, not an unrestricted behavior history. When identity is uncertain, choose a neutral fallback or hold the action instead of forcing a match.
Build an effective-dated evidence contract
| Evidence | Operational use | Freshness or caution |
|---|---|---|
| Message inventory | Define purpose, latency and owner | Include peak and recipient providers |
| Responsibility matrix | Assign every control | Validate contract and technical behavior |
| Route and identity map | Connect domains, IPs and credentials | Every environment and failover |
| Event contract | Process acceptance, deferral, bounce and complaint | Authenticated and idempotent |
| Recovery objective | Design queue, replay and portability | Test exact failure cases |
Every ESP vs SMTP Relay input needs an owner, timestamp, completeness watermark and null behavior. Keep occurrence time separate from ingestion time. A late source should produce an explicit unknown state; treating missing data as a negative signal creates confident but wrong decisions.
Represent the workflow as cancellable states
application or campaign system -> message production
production -> policy, identity and suppression gates
API or SMTP submission -> provider queue
provider MTA -> receiving organization
SMTP + feedback events -> normalized event service
event service -> suppression, analytics, support and incident response
Each ESP vs SMTP Relay transition needs an entry reason, earliest action, useful-until time, cancellation events and terminal state. Re-evaluate current permission, suppression and business state immediately before dispatch. A queue is not authorization to send after the original condition disappears.
Apply hard gates before optimization rules
| Gate | Pass condition | Failure response |
|---|---|---|
| Message purpose | Stream is classified and owned | Do not share ambiguous route |
| Identity | From, DKIM, return path and HELO map | Correct configuration |
| Suppression | Current global state passes | Block promotional dispatch |
| Submission security | TLS, authentication and least privilege pass | Reject client |
| Event readiness | Feedback can be processed before scale | Hold launch |
Hard gates for ESP vs SMTP Relay should be deterministic and observable. A model score, predicted revenue or creative winner cannot override a complaint, applicable unsubscribe, invalid destination, expired event or material data uncertainty. Reserve capacity only after eligibility passes, then release the reservation when the action is canceled.
Implement the system in bounded stages
- Inventory application-generated service mail, bulk promotion, lifecycle, sales and human mailbox needs.
- Build a responsibility matrix for content, consent, list, suppression, DNS, keys, IPs, queues, retries, feedback, support and compliance.
- Prefer provider APIs when they offer stronger idempotency and metadata, but keep SMTP where interoperability or application constraints require it.
- Normalize all provider events into one internal contract and preserve original responses.
- Test outage, failover, credential rotation, provider migration and rollback before production dependency.
Promote the same versioned ESP vs SMTP Relay rules, templates and schemas through test and production. Shadow evaluation before activation reveals population changes without contacting recipients. Start with a bounded cohort whose expected count and provider distribution have been reviewed.
Test data quality at the decision boundary
For ESP vs SMTP Relay, reconcile source records to eligible, excluded, unknown, selected, canceled, attempted, accepted and completed states. Test duplicates, late arrivals, deletion, identity merges, timezone boundaries and one-to-many joins. Sample decisions immediately above and below every threshold.
The team should reproduce why one a message stream and sending identity mapped to an application, provider route and accountable operating team received or did not receive a treatment using the versions and watermarks available at that time. A current dashboard is not sufficient historical evidence for ESP vs SMTP Relay.
Use positive, negative and adversarial fixtures
- The same idempotency key cannot produce duplicate messages after timeout and retry.
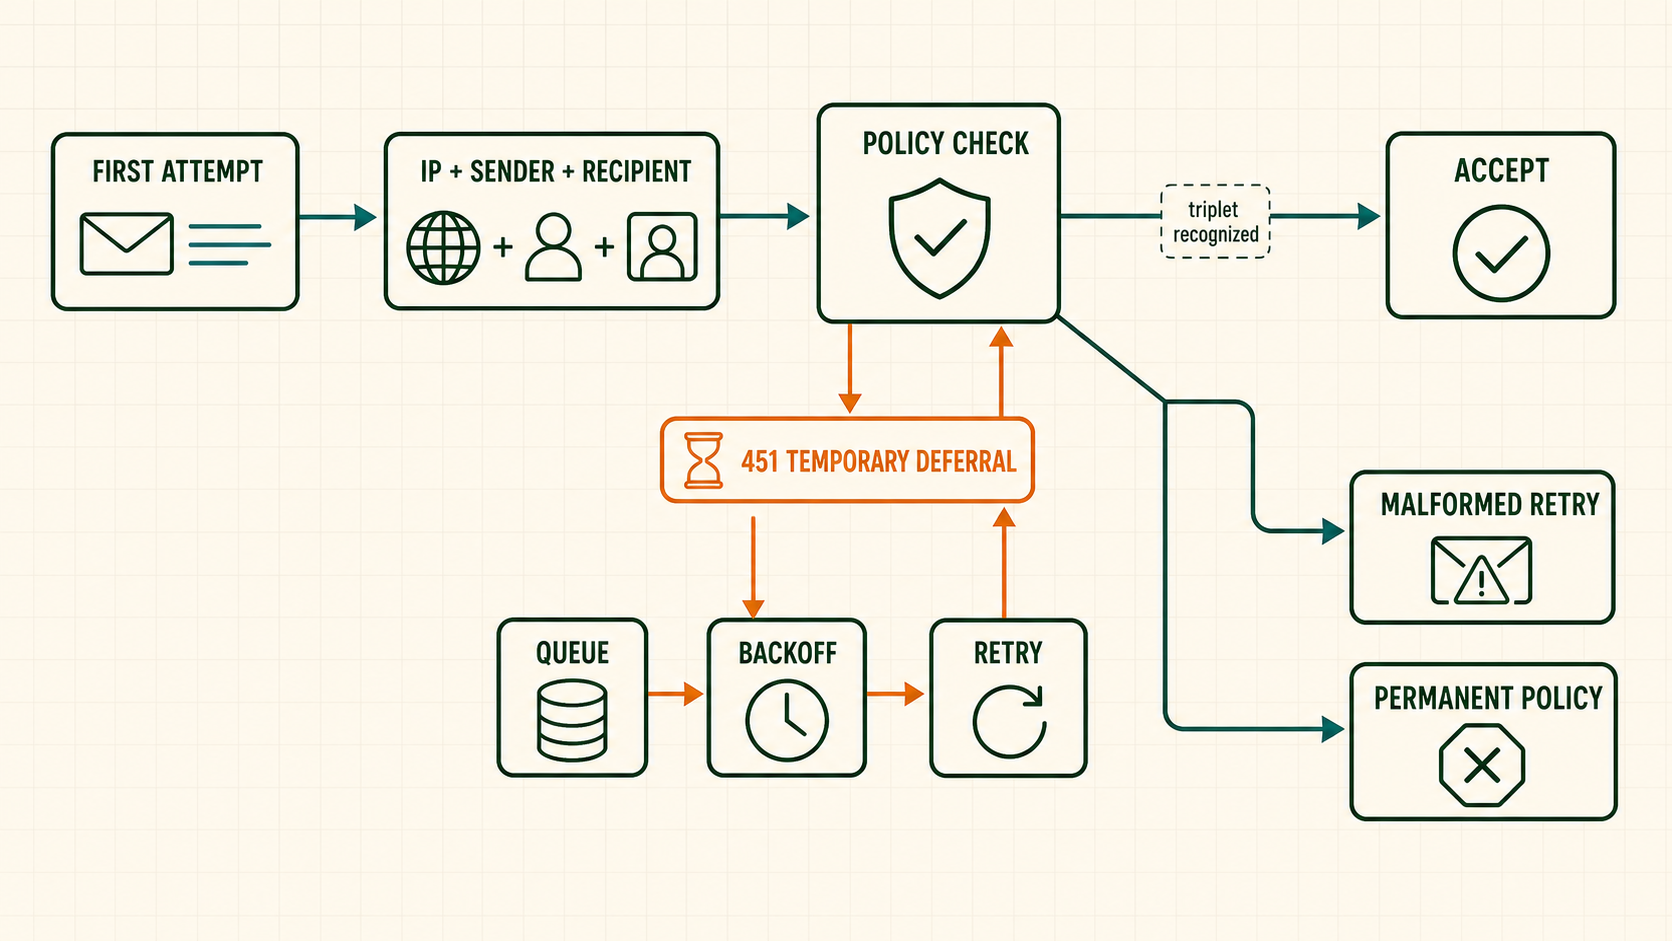
- A 4xx follows bounded retry while a classified 5xx becomes terminal.
- Complaints, hard failures and unsubscribe reach every sending application.
- Failover uses the intended authenticated identity and does not double send queued work.
- Provider export and retention meet incident and migration requirements.
Fixtures for ESP vs SMTP Relay must assert both the selected output and the reason. Run them after changes to data mapping, templates, model versions, providers, links and destination pages. Include accessibility and plain-text behavior, not only a screenshot of the preferred desktop client.
Publish metrics with numerator, denominator and maturity
| Measure | Definition | Decision supported |
|---|---|---|
| Submission acceptance | Provider accepted API or SMTP requests | Client integration |
| Receiver outcomes | 2xx, 4xx and 5xx from receiving systems | Transport operation |
| Queue latency | Time from accepted submission to terminal state | Service objective |
| Feedback latency | Time to normalized bounce, complaint and suppression | Safety |
| Cost per valid message and stream | Provider plus operating cost for mature useful mail | Architecture economics |
Report ESP vs SMTP Relay counts beside rates and expose data latency. Opens are not a reliable universal person-level outcome because images can be blocked or privacy-prefetched. Qualify automated clicks and allow enough time for conversion, cancellation, refund or repeat behavior before declaring business value.
Separate attribution from incrementality
For ESP vs SMTP Relay, last-click and platform-attributed outcomes answer which recorded touch received credit; they do not prove that the treatment caused the outcome. Use randomized treatment and holdout where ethical and practical, keep assignment stable, and prevent equivalent exposure through another journey. If randomization is unavailable, document the comparison design and its remaining bias.
topic = ESP vs SMTP Relay
incremental outcome = treatment outcome rate - holdout outcome rate
incremental value = mature net value in treatment - mature net value in holdout
guardrails = complaints + unsubscribes + support harm + provider failures
Operate by receiving provider and sending stream
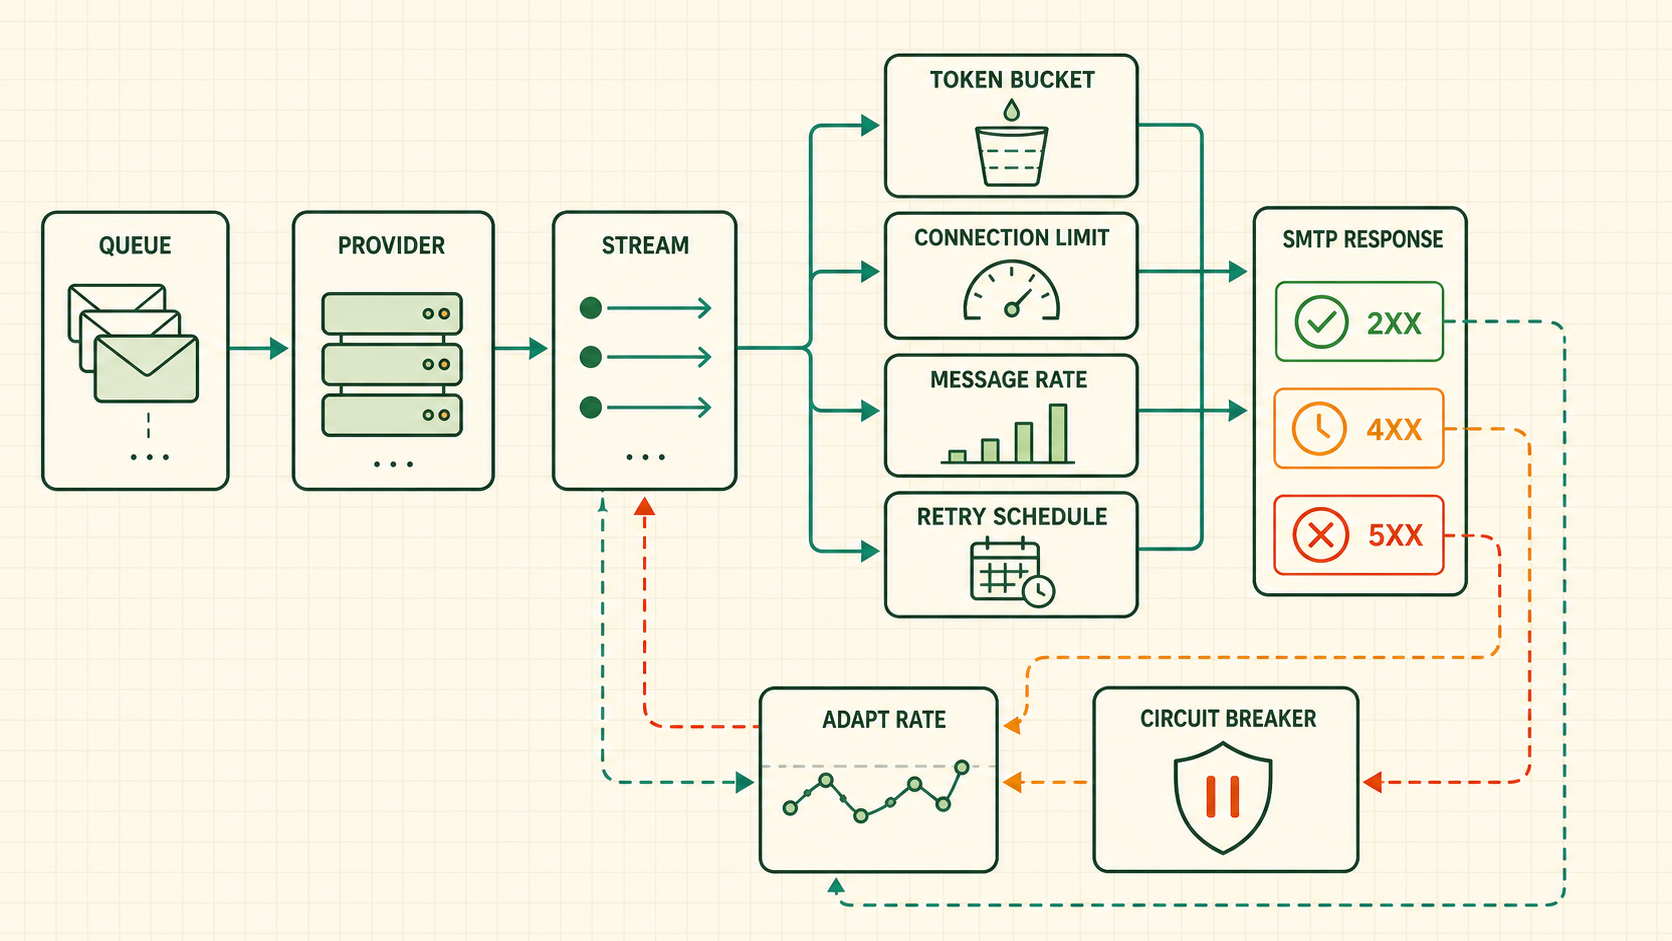
For ESP vs SMTP Relay, forecast attempted volume by receiving organization, hour, identity and message category. Monitor complete SMTP replies, queue age, deferrals, hard failures, complaint signals and authentication results without blending transactional and promotional streams. A healthy global acceptance rate can hide one damaged provider cohort.
Do not rotate domains or IP addresses to escape a ESP vs SMTP Relay permission, targeting or content problem. Reduce the affected population, preserve evidence and correct the cause. Volume increases require stable provider evidence, not a calendar percentage.
Minimize personal data and protect decision artifacts
Collect only data needed for the declared ESP vs SMTP Relay purpose, limit access, define retention and prevent live personal data from entering prompts, tickets, screenshots or test fixtures. Sensitive attributes and inferred vulnerability require stricter review. URLs, tracking parameters and template comments must not expose internal segments or private facts.
Protect ESP vs SMTP Relay webhooks and feedback events with authentication, replay controls and idempotency. A forged conversion, complaint or preference event can select the wrong content or suppress the wrong person. Log decisions without logging secrets.
Make the complete experience understandable and operable
For ESP vs SMTP Relay, use semantic structure, readable hierarchy, sufficient contrast, descriptive links, meaningful image alternatives and a useful plain-text MIME alternative. Keep material conditions and the primary action available without images. Test zoom, image blocking, dark mode, keyboard access to destinations and representative assistive technology.
The ESP vs SMTP Relay accessibility review includes the landing page, preference center, form, checkout and cancellation path. A visually attractive message is not successful when the next step cannot be completed.
Diagnose recurring failure patterns
| Failure | Likely cause | First safe action |
|---|---|---|
| API timeout causes duplicates | No idempotency or reconciliation | Stop replay and reconcile provider IDs |
| Failover fails DMARC | Identity map incomplete | Disable route and correct signing |
| Marketing suppressions miss app mail | Fragmented systems | Centralize applicable policy |
| Vendor dashboard loses detail | Insufficient event retention | Store original event and SMTP text |
| One credential sends all streams | Poor isolation | Create scoped clients and routes |
During a ESP vs SMTP Relay failure, pause the narrowest unsafe cohort or rule. Preserve assignments, source watermarks, selected versions, provider acknowledgements and destination behavior before changing the system. Correct one boundary at a time so recovery evidence remains interpretable.
Scenario: SaaS transactional mail
Password reset and security notices need low latency, idempotency, scoped credentials, event webhooks and stable identities. A transport-focused API may be sufficient when the application owns templates and preferences, but the responsibility matrix still includes feedback and incident support.
Scenario: a marketing team needs lifecycle tooling
The team requires audience management, consent evidence, visual and code templates, experiments, journeys and preference controls. An ESP can reduce application work, while transport identity, data quality and provider monitoring remain jointly operated.
Scenario: dual providers create duplicates
A timeout triggers failover while the primary provider already accepted the message. Without a global idempotency and reconciliation key, both deliver. The architecture adds an internal submission ledger and only fails over terminally unaccepted work.
Contain and recover from a bad release
- Pause the affected rule, cohort, template or route while preserving necessary service communication.
- Capture source watermarks, assignments, artifact versions, queued actions and downstream acknowledgements.
- Apply current complaints, unsubscribes, hard bounces and terminal business events before replay.
- Correct the causal boundary and run the full fixture suite in shadow mode.
- Cancel obsolete work instead of emptying the backlog through stale sends.
- Resume a bounded cohort under provider, complaint and business guardrails.
- Close only after delayed outcomes mature and counts reconcile.
The postmortem for ESP vs SMTP Relay must identify the failed assumption, actual blast radius, customer correction, durable control and owner.
Keep a versioned catalog and decision ledger
Catalog the ESP vs SMTP Relay audience, purpose, permission scope, inputs, precedence, content or rule versions, maximum exposure, experiment, owner, stop condition and retirement date. Detect copied workflows that no longer inherit the approved suppression and frequency policy.
Record each material ESP vs SMTP Relay decision with hypothesis, evidence window, guardrails, uncertainty and resulting action. Expire claims, offers, models and exceptions. Retirement includes disabling triggers, canceling timers and confirming no regional or provider copy remains active.
Create an approval record that can survive an incident
The accountable ESP vs SMTP Relay owner signs the intended recipient benefit, eligibility logic, data versions, message and destination, provider forecast, experiment, safety exclusions, monitoring window and rollback trigger. Data, legal or policy, accessibility, deliverability and business owners approve their boundaries rather than giving a generic campaign approval.
The ESP vs SMTP Relay approval expires when a material audience, claim, source, provider, template, offer or destination changes. Emergency exceptions need a named owner, narrow scope, compensating control and expiry.
ESP vs SMTP Relay release data contract
The release package must make the leading evidence relationship explicit: Message inventory; Define purpose, latency and owner; Include peak and recipient providers. Store the source snapshot, completeness watermark, decision timestamp, rule version, selected reason, exclusion reasons and downstream acknowledgement. Reconcile expected and actual counts before expanding exposure.
Document the owner for every field and what ESP vs SMTP Relay does when the source is missing, late, duplicated or contradictory. The contract should be small enough to review and strong enough to reproduce a customer question months later without querying today current profile.
ESP vs SMTP Relay uncertainty and review cadence
The primary measurement relationship is Submission acceptance; Provider accepted API or SMTP requests; Client integration. Publish uncertainty, data latency and maturity beside it. During launch, review provider and safety evidence at a cadence fast enough to stop harm; after stabilization, move to scheduled drift and cohort reviews without losing alert ownership.
For ESP vs SMTP Relay, compare observed distribution with the approved population and inspect boundary samples. A stable average does not excuse unexplained unknowns, one provider divergence or a small cohort with serious negative outcomes.
ESP vs SMTP Relay capacity and economics
The first implementation priorities are Inventory application-generated service mail, bulk promotion, lifecycle, sales and human mailbox needs.; Build a responsibility matrix for content, consent, list, suppression, DNS, keys, IPs, queues, retries, feedback, support and compliance.. Estimate data, engineering, creative, review, provider, support and incident cost before scaling. Capacity includes human review and customer support, not only messages per hour.
Measure marginal mature ESP vs SMTP Relay value after variable cost and recipient harm. A treatment that increases attributed activity but overloads support, creates refunds or requires constant manual correction is not operationally successful. Record which constraint binds the next release.
ESP vs SMTP Relay retirement and evidence closure
The leading failure pattern is API timeout causes duplicates; No idempotency or reconciliation; Stop replay and reconcile provider IDs. Retirement should stop new selection, cancel obsolete actions, remove copied and regional triggers, disable dependent offers or models, and preserve the final artifact plus aggregate decision evidence. Apply retention and deletion policy to raw personal data.
Confirm that providers, CRM, warehouse, sales automation and preference systems no longer activate the treatment. Close the catalog entry with reason, effective time, owner and any replacement. A hidden orphaned workflow means ESP vs SMTP Relay is still operational.
ESP vs SMTP Relay completion checklist
- Message types, latency, volume and owners are inventoried.
- ESP, relay and protocol terms are used accurately.
- Responsibility matrix covers every lifecycle control.
- Identity and route maps include failover.
- Credentials are scoped by environment and stream.
- Submission uses idempotency and safe retry.
- Receiver outcomes remain visible in original detail.
- Feedback updates suppression promptly.
- Migration and outage recovery are tested.
- Cost includes engineering, support, events and portability.
The ESP vs SMTP Relay implementation is ready only when the team can explain eligibility, treatment, evidence, cancellation and outcome for a real example without relying on a mutable dashboard or undocumented operator knowledge.
Understand the typical ESP control plane
An ESP may manage lists, segmentation, templates, campaigns, journeys, tests, preferences, reporting and sometimes landing pages. It can submit through its own transport or another provider. Feature names do not prove that consent evidence, suppression scope or analytics definitions meet the organization requirements.
Inspect APIs, exports, roles, audit logs, data regions, retention and failure behavior, not only the campaign editor.
Understand the transport-focused relay layer
A relay generally accepts SMTP or API submissions, queues messages, selects outbound infrastructure, handles retries and returns delivery or feedback events. Some relays add templates, analytics or inbound processing. SMTP acceptance by the relay means responsibility transferred to its queue, not that the receiver accepted the message.
Preserve provider message identifiers and downstream SMTP responses for troubleshooting.
Write a responsibility matrix before procurement
For every control, assign customer, provider or shared ownership: consent capture, recipient validation, suppression, content, authentication DNS, DKIM keys, return path, IP reputation, TLS, queue, retry, complaint enrollment, abuse monitoring, data deletion, support and incident communication.
Test each claimed responsibility. A contract statement without accessible event data or an operator process can still leave the customer unable to respond.
Choose API or SMTP submission per application need
APIs can provide structured metadata, idempotency, templates and immediate validation. SMTP offers broad interoperability and well-understood server behavior. Either path requires TLS, scoped authentication, timeout handling, retry ownership and secret rotation.
Do not retry an API timeout blindly if acceptance is unknown. Query or reconcile using a client idempotency key and provider message identifier.
Normalize events without erasing provider evidence
Create internal states for submitted, provider accepted, receiver accepted, deferred, terminal failed, complaint, unsubscribe and suppressed. Store the raw provider event, SMTP code and response text alongside classification and version.
Authenticate webhooks, prevent replay and process idempotently. Classification can change, but raw history should not be silently rewritten.
Score providers with production fixtures
Evaluate identity control, regions, network and IP options, throughput, queue behavior, event latency, retry semantics, complaint support, security, roles, logs, export, retention, support, contract, pricing and exit. Run representative messages and failures through a proof of concept.
A low unit price can be expensive when poor event detail and support extend incidents or require a second platform.
Primary references
- RFC 5321 SMTP
- RFC 5322 Internet Message Format
- RFC 3463 Enhanced Mail System Status Codes
- Gmail sender guidelines
- RFC 8058 One-Click Unsubscribe