ESP and Email Tools: Choosing a Production Stack
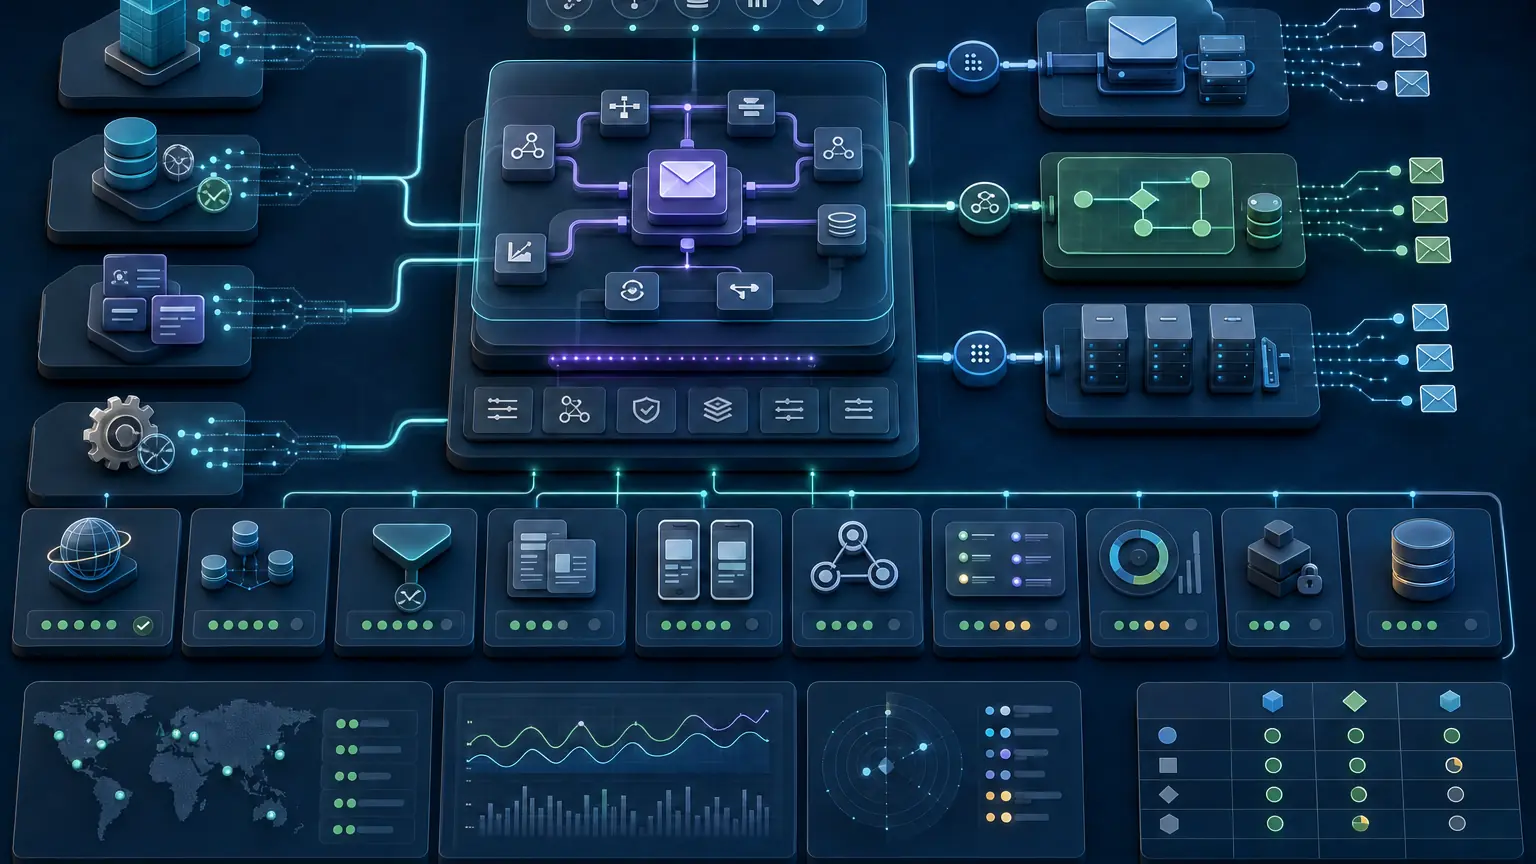
An email service provider is one part of a production email system. Customer data, consent, content, message submission, queues, sender identity, suppression, webhooks, provider feedback, reporting, and incident response must work together. A familiar vendor name or a long feature list does not prove that the complete stack will fit the traffic.
Choose an email service provider from the complete operating path: data and consent, message submission, sender identity, queue behavior, suppression, feedback, reporting, security, support, portability, and incident response. A familiar vendor name, logo wall, or feature count does not prove that the platform fits the traffic.
A vendor directory is not a selection method
The important question is not which platform has the longest feature page. It is whether a proposed stack can accept the required traffic, preserve sender identity, produce trustworthy evidence, enforce consent, survive provider pressure, and let the organization leave without losing critical data.
Begin with the delivery system and its owners. A purchase decision made only by marketing can miss queues, DNS, webhooks, security, data retention, and incident access. A decision made only by engineering can miss journey design, approval, localization, preferences, rendering, and campaign operations. Procurement, security, privacy, support, and deliverability also need explicit review points.
- Describe the message streams, recipients, peak volume, latency, and failure consequences.
- Separate required capabilities from convenient features and speculative future needs.
- Test with representative messages, identities, data, and provider destinations.
- Score evidence from a proof of concept, not a sales demonstration.
- Require an operating owner, an incident path, and an exit plan before signing.
Name the layers before comparing products
The word ESP is often used for several different systems. Naming the layer prevents a feature in one platform from being mistaken for a control somewhere else.
| Layer | Primary job | Questions it must answer |
|---|---|---|
| Delivery API or SMTP relay | Accept messages, queue them, deliver them, and return transport events | How are retries, IP pools, streams, domains, responses, suppressions, and webhooks controlled? |
| Marketing automation or customer engagement | Build audiences, journeys, campaigns, preferences, and personalized content | Which data is authoritative, how is consent enforced, and what reaches the delivery layer? |
| CRM or customer data platform | Store customer and account context, segments, and business events | Which identifiers, permissions, timestamps, and source records are synchronized? |
| Mail transfer agent | Operate SMTP queues, routing, retry, concurrency, and delivery policy | Who owns capacity, security, upgrades, traffic shaping, logs, and provider response? |
| Content and pre-send system | Build, approve, render, test, and version messages | Can it test real personalized output, accessibility, links, dark mode, and important clients? |
| Provider-native diagnostics | Expose provider-specific reputation, complaint, authentication, and delivery evidence | Which domains or IPs are covered, what thresholds apply, and how delayed is the data? |
| Event and observability platform | Normalize evidence, retain history, alert, and support investigation | Can raw responses be reconstructed across recipient, message, stream, provider, identity, and time? |
One suite may cover several layers, but the responsibilities remain distinct. A journey tool does not become a transport queue merely because it displays a delivery status. An email preview does not prove inbox placement. A CRM consent field does not enforce suppression unless the sending path actually checks it.
Start with traffic and business requirements
Inventory what must be sent before discussing architecture. Use measured production behavior where possible, including normal volume, peak bursts, message size, personalization time, recipient mix, seasonal changes, and required retention.
| Stream | Typical requirement | Failure consequence |
|---|---|---|
| Security and access | Low latency, high availability, short usefulness window, tight template control | A user cannot sign in, verify an action, or recover an account |
| Transactional | Application events, durable submission, idempotency, accurate status, long audit trail | A receipt, booking, shipment, or account notice is late or missing |
| Lifecycle | Customer state, journey rules, frequency control, preferences, experimentation | The message is mistimed, duplicated, irrelevant, or inconsistent with consent |
| Promotional | Audience selection, approvals, scheduling, unsubscribe enforcement, volume management | Complaints, policy pressure, wasted spend, and brand harm increase |
| Support and operational | Conversation context, ticket integration, controlled identities, human workflow | Responses lose context or expose the wrong address or account |
Record data sensitivity, countries, legal entities, brands, business units, tenants, and required data residency. Define recovery time and recovery point needs. Ask which messages can be delayed, which can be regenerated, and which must never be duplicated. These requirements determine architecture more reliably than a generic feature checklist.
Map streams before assigning vendors
Traffic separation is an operating control, not a cosmetic account setting. Security notifications should not share every fate with a large promotional send. Separate streams in the data model, submission credentials, configuration, reporting, and suppression policy before considering separate domains or IP pools.
A stream map should connect the visible From domain, DKIM signing domain and selector, Mail From or return-path domain, tracking domain, submission route, IP pool, reply handling, unsubscribe behavior, suppression scope, webhook destination, data owner, and incident owner. The email infrastructure guide explains why these identities and transport layers must be reviewed as one path.
Dedicated IPs are not an automatic upgrade. They provide more direct ownership of an IP reputation, but they also require sufficient stable traffic, controlled warmup, provider-aware shaping, monitoring, and operational coverage. A managed shared pool can be the safer choice for low or irregular volume. Require the vendor to explain pool placement and movement rules instead of treating shared and dedicated as simple quality tiers.
Choose an architecture pattern deliberately
| Pattern | Useful when | Principal cost or risk |
|---|---|---|
| One managed suite | Journeys, content, submission, and reporting need one operating surface | Deeper coupling, constrained transport evidence, and a harder exit if data or identities are not portable |
| Engagement platform plus delivery service | Marketing needs journey tooling while engineers need stronger delivery APIs or transactional separation | Consent, message identity, suppression, and events must remain consistent across two systems |
| Separate transactional and marketing providers | The streams have materially different latency, teams, risk, or lifecycle needs | Duplicate integrations, fragmented evidence, and identity governance across vendors |
| Multiple delivery providers | There is a tested continuity, regional, product, or negotiating requirement | More domains, pools, classifiers, event schemas, suppression synchronization, and failover states |
| Self-managed MTA | The organization needs deep queue, routing, policy, cost, or data control and can operate it continuously | Capacity, security, upgrades, abuse prevention, shaping, logging, reputation, and on-call ownership stay internal |
| Hybrid managed and self-managed | Selected streams need custom control while others benefit from managed operations | The boundary and evidence model can become more complex than either system alone |
Multi-provider routing does not automatically improve deliverability. It can preserve a submission path during a platform incident, but an identity, consent, content, or reputation failure may follow the traffic to the second provider. Failover without synchronized suppression and complete event correlation can also create duplicates or contact people who must not receive the message.
Build a capability and evidence matrix
Convert requirements into testable rows. Mark each row as native, configuration-dependent, custom integration, partner feature, unavailable, or unverified. Assign an owner and evidence source.
| Area | Capabilities to verify | Evidence to request |
|---|---|---|
| Identity | Custom DKIM, aligned return path, tracking domains, selector rotation, domain separation | DNS plan, received headers, rotation procedure, and asset ownership |
| Submission and queues | API and SMTP behavior, idempotency, rate limits, retry schedule, queue lifetime, priority | Load test, error responses, retry observation, queue visibility, and incident procedure |
| Traffic controls | Streams, pools, tenants, throttles, provider shaping, warmup, pause and resume | Configuration export, role test, change log, and controlled deferral exercise |
| Events | Raw SMTP response, enhanced code, phase, attempt, recipient, provider, IP, stream, timestamps | Real payloads, schema, retention, replay, duplicate handling, and export |
| Consent and suppression | Purpose and brand scope, complaint, unsubscribe, invalid recipient, temporary hold, audit | End-to-end test, import and export, precedence rules, and correction workflow |
| Content | Versioning, approvals, localization, personalization, accessibility, rendering, link checks | Largest realistic message, approval history, plain-text part, and client previews |
| Security and privacy | SSO, MFA, RBAC, scoped credentials, webhook protection, encryption, residency, deletion | Architecture, access test, audit log, DPA, subprocessor list, and deletion evidence |
| Operations and exit | Status, support, incident access, data portability, domain release, configuration export | Support exercise, full export, recovery test, ownership schedule, and contract terms |
Use current products as examples, not rankings
Product names help define the market, but categories overlap and features change. The examples below are starting points for a current evaluation, not endorsements or a claim that every product fits every row.
- Managed delivery APIs and relays: Amazon SES, Mailgun, Postmark, and Twilio SendGrid expose API or SMTP submission with different approaches to streams, pools, events, retention, and support.
- Customer engagement and marketing suites: Braze, Iterable, Klaviyo, and Salesforce Marketing Cloud combine email with audience, journey, campaign, and cross-channel functions in different ways.
- Self-managed transfer: Postfix is a general-purpose open-source MTA. KumoMTA documents queues, sources, pools, automation, and traffic shaping for high-volume operations. Commercial MTAs provide another procurement path.
- Pre-send inspection: systems such as Mailgun Inspect, specialist rendering products, accessibility tools, link checkers, and maintained test accounts can provide complementary evidence.
- Mailbox-provider evidence: Google Postmaster Tools, Microsoft SNDS and JMRP, and Yahoo Sender Hub expose provider-specific signals that no ESP can recreate independently.
Confirm current documentation, contracts, pricing, regional availability, support, and limits directly with each supplier. Product packaging can change faster than a procurement cycle.
Confirm current documentation, contracts, pricing, regional availability, support, and limits directly with each supplier before evaluation or purchase.
Keep sending identity under organizational control
Do not let convenience turn the vendor into the only party that controls the identity. The organization should know who owns and can change every sending domain, DKIM key and selector, return path, tracking domain, TLS certificate, reverse DNS entry, complaint-program enrollment, and provider diagnostic account.
- Use organization-controlled domains and delegated subdomains with documented DNS ownership.
- Record which party generates, stores, rotates, and revokes DKIM private keys.
- Require aligned custom identities where the traffic and provider support allow them.
- Keep provider accounts and feedback programs in controlled organizational accounts, not personal logins.
- Document how identities and certificates are released, migrated, or revoked at contract end.
A platform can simplify DNS setup, but the final proof is a received message. Inspect SPF, DKIM, DMARC, the visible From domain, Mail From, Message-ID, links, and unsubscribe behavior through each real stream. Use the authentication diagnostic guide when setup screens and received results disagree.
Evaluate submission, queues, retries, and rate control
Test both successful and failed submission. An API should expose stable identifiers, documented error bodies, timeouts, rate behavior, and an idempotency strategy. SMTP submission should have clear authentication, TLS, response, size, and concurrency behavior. A client timeout must not leave the application guessing whether the platform accepted the message.
Managed systems often hide queue mechanics, but the operating questions remain. Determine how long temporary failures retry, whether queue lifetime can vary by stream, how provider throttling changes delivery rate, what happens during an account pause, and whether queued messages can be searched, cancelled, or expired safely. Amazon SES documents managed and dedicated IP pools; KumoMTA documents traffic shaping. The existence of a control is not proof that its default is right for the traffic.
Test realistic peaks rather than multiplying average volume. Include the largest personalized message, slow upstream data, provider 4xx replies, credentials that expire, DNS failure, webhook delay, and a pause during an active queue.
Demand a complete event model
A platform event named delivered usually means that a receiving SMTP system accepted the message. It does not prove inbox placement, display, reading, or a human action. Keep submission acceptance, processing, SMTP delivery, deferral, failure, complaint, unsubscribe, placement testing, and engagement as distinct event families.
| Event question | Minimum useful fields | Common mistake |
|---|---|---|
| What was submitted? | Internal message key, provider message key, recipient, stream, tenant, template version, submission time | Keeping only campaign totals |
| What did SMTP report? | Attempt time, SMTP phase, reply, enhanced status, remote site, source IP, route, queue age | Replacing raw evidence with hard or soft |
| What action followed? | Retry, expiry, suppression, hold, release, rule version, actor, timestamp | Assuming a failed event always means invalid recipient |
| Can it be correlated? | Stable IDs across application, provider, webhook, MTA, campaign, and recipient | Using an email address and timestamp as the only join |
| Can it be replayed? | Raw event, signature context, idempotency key, schema version, retention, backfill method | Assuming webhooks arrive once and in order |
Twilio SendGrid documents event identifiers that can support duplicate detection. Postmark documents webhook retries and recommends idempotent handling. Security methods vary by supplier: some support signed requests, while others rely on controls such as HTTPS, basic authentication, source restrictions, or payload verification. Test the actual method instead of requiring a checkbox with no end-to-end proof.
Design consent and suppression boundaries
A single global suppressed flag is rarely enough. Unsubscribe, complaint, invalid recipient, temporary mailbox issue, legal hold, frequency preference, provider block, identity failure, and message failure have different causes and release conditions.
Define whether a state applies to one address, person, account, tenant, brand, purpose, stream, domain, provider, route, or the whole organization. Record the source, evidence, time, policy version, owner, expiry where applicable, and approved correction path. A platform must prevent a campaign import, API call, failover provider, or manual send from bypassing the required state.
Export and reimport the complete model during the proof of concept. A CSV containing only address and reason may lose tenant, purpose, timestamp, evidence, or precedence. The bounce-handling guide provides a detailed framework for classifying transport evidence without deleting valid recipients.
Use mailbox-provider tools directly
ESP dashboards are useful, but the provider receiving the traffic has evidence the sender cannot infer from opens or vendor-wide averages.
- Google Postmaster Tools can expose domain and IP reputation, reported spam, authentication, encryption, delivery errors, and compliance information for eligible traffic. Google notes that data is not real time and may be absent below privacy or volume thresholds.
- Microsoft Smart Network Data Services provides Outlook.com data associated with enrolled IP space. The Junk Mail Reporting Program adds complaint reports for eligible senders.
- Yahoo Sender Hub provides sender resources, complaint feedback enrollment, and domain-level delivery insights subject to its requirements.
These systems are provider-specific. Missing dashboard data does not prove that traffic is healthy, and one provider result does not describe another. Keep organizational ownership and access continuity even if an ESP helps with setup. The sender reputation guide explains how to combine these signals without manufacturing one universal score.
Treat pre-send testing as bounded evidence
A test system can find broken links, malformed HTML, accessibility problems, dark-mode surprises, blocked remote assets, and client-specific rendering defects. It cannot guarantee how every personalized message will render or where a later production message will be placed.
Test the final message after real personalization, tracking rewrites, localization, and footer insertion. Include webmail, desktop, and mobile-app views important to the audience. Review narrow widths, zoom, dark mode, keyboard use, screen-reader structure, image blocking, plain text, long URLs, large fonts, and touch targets. The email build guide covers these checks, including whitespace, commented code, link handling, mobile application views, and clipping caused by large messages.
Seed tests and inbox-placement panels are samples. Their accounts, filters, timing, and engagement history are not the production audience. Use them to compare controlled changes, not as a percentage promise for the next campaign.
Review security, privacy, and governance
Email platforms process addresses, content, behavioral events, account attributes, and sometimes highly sensitive transactional data. Review the complete data path, including subprocessors, support tools, backups, exports, analytics, and webhook destinations.
- Require SSO and MFA where available, role-based access, scoped API credentials, short-lived access where practical, and auditable administrative actions.
- Separate production, test, tenant, agency, and business-unit access. Test whether a user can export or send outside the intended scope.
- Rotate credentials and signing secrets without stopping mail. Inventory credentials embedded in applications and automation.
- Document data locations, retention, deletion, legal hold, encryption, incident notification, and subprocessor changes.
- Minimize sensitive data in templates, metadata, event payloads, logs, and URLs.
- Validate webhook authenticity and replay resistance using the method the selected platform actually supports.
Use the email security and privacy guide for a wider review of identity, transport, content, tracking, and account controls.
Calculate the full operating cost
Message price is only one line. Build a three-year model using expected and peak volume, regions, support level, and growth scenarios.
- Base subscription, message volume, contacts, seats, workspaces, and overage bands
- Dedicated IPs, warmup, validation, rendering, analytics, event retention, and premium support
- Implementation, data mapping, templates, domains, security review, training, and procurement
- Ongoing engineering, campaign operations, deliverability, on-call support, monitoring, and data storage
- Parallel operation, contract overlap, migration, archive, and decommissioning
- Incident cost when queues, credentials, provider access, or suppression synchronization fail
A lower unit rate can be expensive if evidence must be rebuilt externally. A larger suite can also be wasteful when most licensed features remain unused. Model the people and controls needed to operate the proposed architecture, not only the invoice.
Run a production-like proof of concept
A useful proof of concept sends enough controlled traffic to test the system, but it does not risk an uncontrolled migration. Agree on success criteria and evidence before the vendor configures the demonstration.
| Test | What to observe | Passing evidence |
|---|---|---|
| Identity | Custom domains, alignment, selector and credential rotation | Received headers, DNS inventory, rotation and rollback exercise |
| Message construction | Largest personalization, localization, plain text, links, unsubscribe, mobile rendering | Approved final artifacts and received-message review |
| Transport pressure | Burst submission, timeouts, 4xx deferrals, retry, pause, queue expiry | Stable identifiers, no duplicate send, visible queue state, documented outcome |
| Event pipeline | Duplicate, delayed, reordered, malformed, and missing webhooks | Idempotent state, alert, replay, reconciliation, and raw evidence |
| Suppression | Unsubscribe, complaint, invalid address, temporary hold, import, export, failover | Correct scope, audit history, no bypass, and reversible valid state |
| Provider evidence | Gmail, Outlook.com, Yahoo, and other material destinations | Provider-specific results correlated to stream, identity, IP, and time |
| Security and operations | Roles, credential loss, support escalation, status incident, configuration change | Controlled access, audit logs, named escalation, rollback, and runbook |
| Exit | Full data, content, suppression, event, and configuration export | Usable files, documented gaps, identity release, and verified import path |
Do not score only whether a feature exists. Score whether the team can operate it, prove it, recover it, and explain its limits.
Plan migration and exit before purchase
Keep an independent inventory of domains, DNS, authentication, pools, streams, credentials, templates, suppression states, consent sources, event schemas, provider accounts, and owners. Decide which system is authoritative for each object. Version configurations outside a single vendor interface where possible.
A migration needs parallel event reconciliation, controlled volume movement, identity warmup where appropriate, provider monitoring, and a rollback threshold. Do not move all traffic because a small seed test looked normal. Preserve historical evidence long enough to compare the old and new routes and investigate delayed events.
The exit clause should cover configuration and data exports, retention after termination, custom-domain release, dedicated-IP handling, support during transition, deletion evidence, and access to historical events. Portability tested before the contract is more reliable than an assurance requested during an incident.
Production selection checklist
- Inventory streams, recipients, peaks, latency, message size, regions, sensitivity, and failure impact.
- Name every required layer and assign an organizational owner.
- Map visible From, DKIM, Mail From, tracking, IP pool, reply, suppression, event, and provider identities.
- Choose an architecture pattern from requirements, not vendor familiarity.
- Build a scored capability matrix with evidence, owner, and unresolved risk for every row.
- Keep domains, DNS, provider programs, certificates, and critical identities under organizational control.
- Test submission ambiguity, queues, retries, provider throttling, pause, and expiry.
- Require raw transport evidence, stable identifiers, replay, retention, and idempotent webhook handling.
- Prove consent and suppression boundaries across campaigns, APIs, imports, and failover paths.
- Use Google, Microsoft, Yahoo, and other material provider diagnostics directly.
- Test final personalized messages across important webmail, desktop, and mobile-app surfaces.
- Review SSO, MFA, roles, credentials, webhook protection, privacy, residency, deletion, and audit.
- Model the full operating cost, including people, evidence, support, migration, and incidents.
- Run a production-like proof of concept with agreed passing evidence.
- Test a full export, recovery procedure, identity release, and exit path before commitment.
The best email stack is not the one with the most logos around it. It is the one whose boundaries are understood, whose evidence survives an incident, and whose owners can change or leave it safely. NitWings can help with multi-ESP and custom MTA architecture when the decision spans traffic separation, sender identity, delivery infrastructure, event normalization, migration, or production validation.
ESP and email tools directory
Explore mailbox providers, email service providers, and supporting email tools. Website status was checked on 10 August 2026 UTC. Status describes the listed website response, not the company's legal or operating status.
Browse 571 providers in three categories.
No providers match this search.
Mailbox providers (MBP)53 providers
 Amazon WorkMailLive | ||