
Gmail BIMI Verified Checkmarks in 2023: VMC-Based Brand Verification
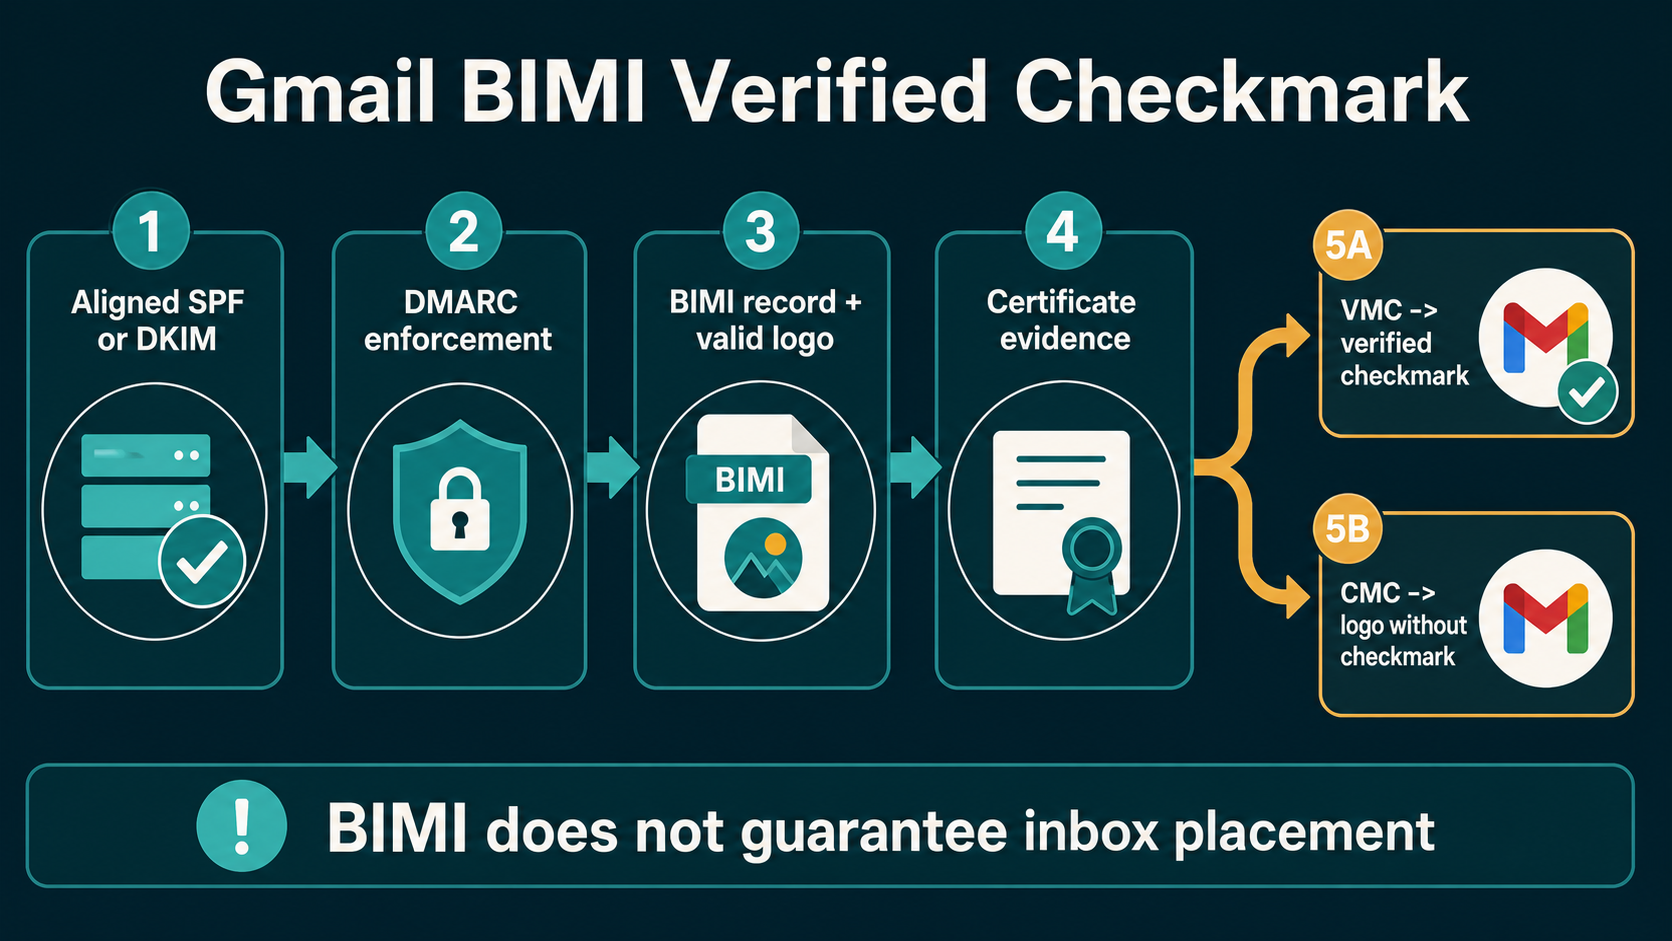
Google began rolling out a checkmark icon for eligible BIMI senders in Gmail on May 3, 2023. At launch, the checkmark was tied to a Verified Mark Certificate path layered on DMARC and BIMI. The visible cue helped users recognize that Google had validated the logo evidence used for that organizational identity. It did not certify the campaign, protect a sender from normal spam filtering or guarantee that every Gmail interface would display the mark. Later Gmail support for Common Mark Certificates introduced an important distinction: a supported logo may appear without the verified checkmark. Operators therefore need separate controls for authentication, BIMI eligibility, logo evidence and checkmark status.
The dated mailbox-provider change
| Event field | Verified value | Why it matters |
|---|---|---|
| Historical event date | May 3, 2023 | This is the provider-change date, not the NitWings publication date. |
| Mailbox provider | Gmail | The affected provider estate determines which recipient cohorts require separate evidence. |
| Change area | Brand identity | This identifies whether the change altered authentication, filtering, visibility, measurement or sender operations. |
| Current status | active-vmc-backed-checkmark-with-later-cmc-logo-option-without-checkmark | Historical instructions are interpreted against the feature or standard that exists now. |
Gmail launched general BIMI support in 2021, allowing eligible senders to present brand-controlled logos after strong authentication and certificate validation.
The 2023 checkmark added an explicit interface indicator next to qualifying VMC-backed senders. It made evidence type visible to recipients rather than leaving the logo as the only cue.
Subsequent CMC support widened logo options but did not make every certificate path equivalent to the verified checkmark.
This event is best understood as a change in one layer of the email system. Transport acceptance, authentication, placement, interface presentation and user action remain different states. The article therefore records what Gmail BIMI verified checkmark changed and what it did not change.
How the system worked before the change
An eligible VMC-backed BIMI logo could appear in Gmail, but the sender row lacked this newly announced checkmark indicator.
Teams often collapsed DMARC pass, BIMI DNS validity, logo display and inbox placement into one success state. That made missing-logo incidents expensive and imprecise.
Certificate purchasing sometimes began before all visible From domains and organizational relationships were inventoried.
Before Gmail BIMI verified checkmark, teams often had incomplete evidence because sender logs ended at SMTP acceptance while recipient-side behavior occurred inside Gmail. That boundary matters: an accepted message can still be filtered, presented differently, ignored or acted upon later.
What changed on the provider side
Gmail added a checkmark icon for senders that had adopted BIMI using a VMC and met Google’s requirements. The rollout applied across supported Gmail surfaces.
The indicator strengthened a provider-controlled identity signal. It did not review each message’s commercial truth or user consent.
Later certificate choices mean operators must not document “BIMI logo” and “verified checkmark” as synonyms.
The implementation of Gmail BIMI verified checkmark created a new operating dependency, not a permanent entitlement. Senders still needed controlled rollout, supported fallbacks, reliable identity and evidence from the actual affected cohort.
Message path before and after
Before
Aligned authentication -> DMARC enforcement -> BIMI + VMC
Gmail eligibility checks -> logo may display
No separate verified-checkmark indicator
After
Aligned SPF or DKIM -> DMARC enforcement
BIMI assertion -> valid SVG -> acceptable evidence
VMC-backed eligible path -> Gmail logo plus verified checkmark may display
CMC-supported path -> logo may display without verified checkmark
Who and what the change affected
| Traffic or stakeholder | What changed | Required interpretation |
|---|---|---|
| Recipients in the affected provider surface | Gmail BIMI verified checkmark changed what the mailbox could display, infer or act upon. | Segment evidence by supported client, account and provider estate. |
| Permission-based senders | A new capability or recipient signal entered the message path. | Consent, expectation and normal filtering still apply. |
| Deliverability operators | Diagnosis gained another provider-controlled state. | Keep acceptance, placement, presentation and engagement separate. |
| Campaign and lifecycle teams | Message design or timing needed a compatible operating rule. | Protect transactional purpose, suppression and fallback behavior. |
| Data and analytics teams | Historical metrics could change meaning or coverage. | Version definitions and do not compare incompatible populations. |
| Security and privacy owners | The trust or data boundary changed. | Approve endpoints, access, retention and exception handling. |
Effect on delivery, placement and recipient visibility
Diagnose a missing mark using a dependency tree. Start with message-level authentication, then organizational-domain alignment, DMARC policy, BIMI lookup, SVG, certificate chain, provider eligibility and client surface.
Do not compare a VMC sender with a CMC sender as though the visual outcomes were designed to be identical.
For Gmail BIMI verified checkmark, BIMI is a presentation layer built on authenticated identity. DMARC enforcement, aligned authentication, logo evidence, DNS publication and provider eligibility are prerequisites, but none of them guarantee inbox placement or a particular mailbox category. Normal reputation and abuse systems still apply.
For Gmail BIMI verified checkmark, The visible logo must correspond to the organizational domain evaluated by the receiver. A parent-company certificate does not automatically cover every sending domain, and a technically valid SVG does not prove that the provider will display it. Domain inventory and certificate coverage must precede rollout.
For Gmail BIMI verified checkmark, A missing logo is not proof of delivery failure. Causes include unsupported clients, cache delay, record errors, certificate or evidence problems, DMARC failure, provider reputation decisions and message-specific identity alignment. Diagnose the chain in that order rather than repeatedly changing creative.
Interpret Gmail BIMI verified checkmark at the smallest defensible unit: provider, recipient domain, stream, sending domain, DKIM identity, IP pool, campaign and time window. Portfolio averages can hide both a provider-specific regression and an improvement limited to one eligible surface.
Effect on measurement and diagnosis
Maintain screenshots and raw headers from controlled accounts, with client and timestamp. A certificate validation tool cannot prove the provider actually rendered the mark.
Evaluate downstream trust and impersonation outcomes over a complete window. Do not use an open-rate spike as direct evidence of checkmark exposure.
When measuring Gmail BIMI verified checkmark, Measure BIMI as a trust and recognition experiment, not as a deliverability certification. Compare eligible and non-eligible surfaces with careful client segmentation, then examine clicks, conversions, complaints and reported impersonation alongside opens.
When measuring Gmail BIMI verified checkmark, Logo impressions are generally not a sender-controlled event stream. Provider rendering is conditional and cached, so absence of a logo-view counter does not justify embedding new tracking into the logo asset. Use DNS, certificate, authentication and controlled mailbox evidence.
Create an evidence contract before declaring the impact of Gmail BIMI verified checkmark. Name the event, collection point, population, numerator, denominator, latency, privacy boundary and owner. If any of those are unknown, label the conclusion as directional rather than causal.
Advantages for email marketers
| Potential advantage | When the advantage is real | Evidence to verify |
|---|---|---|
| Clearer recipient experience | The message is expected, authenticated and supported. | User outcomes improve without complaint growth. |
| Better operational evidence | Provider and sender states remain separately observable. | Incidents can be isolated to a specific layer. |
| Stronger identity or control | Configuration matches the verified organizational domain. | Authentication and trust checks remain stable. |
| Safer optimization | A controlled cohort and complete window are used. | Clicks, conversions and complaints support the decision. |
| Repeatable deployment | Ownership, rollback and monitoring are documented. | A second team can reproduce the result. |
Disadvantages and operational risks
| Cost or risk | How it appears | Control |
|---|---|---|
| Capability is mistaken for allowlisting | Teams expect placement without reputation discipline. | State explicitly that normal filtering continues. |
| Unsupported clients receive a broken experience | Content or action disappears outside the target surface. | Maintain and test a complete fallback. |
| A proxy metric becomes business truth | A UI or collection change looks like performance. | Use named denominators and downstream outcomes. |
| Too many variables change together | No cause can be assigned after a regression. | Use a staged rollout with rollback thresholds. |
| Provider-specific behavior is generalized | One domain trend is applied to the full list. | Segment by recipient provider and supported surface. |
| Exceptions outlive their reason | Allow lists, access or configuration increase risk. | Assign an owner, expiry and periodic review. |
What email teams needed to do at the time
- Confirm the historical scope. Record the announced provider, date, clients and eligibility.
- Inventory affected traffic. Map recipient domains, streams, identities and sending platforms.
- Validate authentication. Check SPF, DKIM, DMARC alignment and TLS independently.
- Build a safe fallback. Keep the message useful when the new surface is unavailable.
- Test controlled mailboxes. Capture headers, screenshots, timestamps and outcomes.
- Define measurement. Name populations, denominators, latency and privacy limits.
- Stage the rollout. Change one bounded cohort and set stop conditions.
- Brief support teams. Give them expected behavior and an escalation evidence pack.
What email teams should do now
- Read the current provider documentation. Do not assume the 2020 to 2022 launch rules are unchanged.
- Reconfirm eligibility and support. Test the exact clients, accounts and sending identities in use.
- Keep authentication aligned. Monitor SPF, DKIM, DMARC and TLS as separate controls.
- Preserve permission evidence. A presentation feature does not repair weak acquisition.
- Segment provider traffic. Diagnose Gmail separately before changing global policy.
- Protect suppressions and transactional streams. Do not let experimentation delay required state changes.
- Retain raw evidence. Store message IDs, timestamps, headers, configuration and test results.
- Use outcome metrics. Include clicks, conversions, complaints, opt-outs and support impact.
- Review security and privacy. Limit data, endpoints, credentials and exceptions.
- Maintain rollback. Name the owner and the threshold that returns traffic to the known-safe path.
Worked deliverability scenario
A group buys one VMC and expects a checkmark for several regional From domains. The primary brand works, while a recently acquired domain shows neither the logo nor mark.
Authentication samples reveal aligned DKIM, but the acquired domain is absent from the certificate and publishes an incorrect BIMI location. The team corrects domain evidence instead of warming a new IP.
A matrix records VMC, CMC, logo and checkmark states separately. Stakeholders receive an accurate eligibility report without an inbox-placement promise.
The decisive improvement for Gmail BIMI verified checkmark is operational: the team separates provider evidence from assumptions, changes one controlled variable, records a rollback threshold and waits for a complete observation window. That prevents a visible interface change from becoming an excuse for unrelated domain, volume or creative changes.
Evidence and diagnostics
- Message identity: RFC 5322 From, envelope sender, DKIM domain and selector.
- Transport: connecting IP, TLS result, SMTP response and provider timestamp.
- Authentication: SPF, DKIM, DMARC and ARC results from the received header.
- Eligibility: provider registration, tenant setting, certificate or supported-client state.
- Rendering: raw MIME, fallback, screenshots and client version.
- Recipient scope: provider domain, account type, geography and app surface.
- Behavior: clicks, replies, conversions, complaints and unsubscribes.
- Change record: deployment time, owner, cohort, configuration diff and rollback threshold.
- Comparison: unaffected control cohort with the same purpose and acquisition source.
Failure modes and incorrect conclusions
- Equating SMTP acceptance with inbox placement. These are separate receiver decisions.
- Calling a provider UI change a reputation penalty. Verify transport and folder evidence first.
- Removing the fallback. Support and eligibility are never universal.
- Changing IP, domain, creative and cadence together. The test becomes uninterpretable.
- Trusting opens as the only outcome. Collection and privacy controls distort them.
- Ignoring the recipient denominator. Portfolio averages conceal provider-specific effects.
- Keeping permanent exceptions. Unowned allow lists and credentials accumulate risk.
- Using launch documentation as current policy. Recheck the maintained provider page.
Current status and superseding changes
Gmail continues to support BIMI and distinguishes certificate-backed presentation paths. Google’s current administrator guidance governs DMARC, logo and certificate requirements.
Certificate products and provider rules can change. Confirm trademark or domain-control evidence, coverage and renewal operations before committing budget.
Current behavior for Gmail BIMI verified checkmark must be checked again before a production change because provider documentation, client support and eligibility can evolve. The dated event remains useful as a historical control point, while the linked current documentation governs present operation.
A production runbook for Gmail BIMI verified checkmark should contain more than a setup instruction. Record the business purpose, accountable owner, approved sending identities, affected recipient population, prerequisites, evidence sources, known unsupported paths, rollout cohort, stop threshold and rollback method. Attach a dated configuration export or DNS answer instead of relying on a screenshot with no timestamp. Review the runbook after an ESP, gateway, domain, certificate, mailbox client or provider policy changes.
Incident handling for Gmail BIMI verified checkmark should begin with a narrow comparison. Select one affected message and one known-good message with the same stream and nearby time. Compare SMTP responses, authentication results, raw MIME, provider or tenant eligibility, client presentation and downstream action. Widen the query only after identifying the first state where their paths differ. This is faster and safer than changing sending IPs, From domains and creative together.
Ownership for Gmail BIMI verified checkmark must cross organizational boundaries. Deliverability owns provider evidence and traffic controls; engineering owns MIME, APIs and event integrity; security owns trust and endpoint risk; privacy owns collection and retention; marketing owns permission, promise and cadence; support owns recipient-facing explanations. A launch is incomplete when any team lacks the evidence required to distinguish expected behavior from failure.
Evidence for Gmail BIMI verified checkmark also needs a retention rule. Keep enough raw headers, configuration history and aggregate outcome data to investigate a delayed complaint or regression, but do not retain recipient-level data merely because it was convenient during launch. Limit access by role, document the permitted purpose, remove expired exports and preserve only the minimum artifacts needed to reproduce the operational conclusion.
Finally, retain a negative control for Gmail BIMI verified checkmark. Send a technically valid message that is intentionally outside the feature’s eligible condition, while keeping purpose and audience comparable. The difference shows whether Gmail is applying the feature where expected. It also prevents teams from interpreting an unrelated seasonal, audience or reputation shift as proof that the feature caused the result.
Operator checklist
- Record the exact historical event date and source.
- Document what changed and what explicitly did not change.
- Map affected providers, domains, clients and account types.
- Validate SPF, DKIM, DMARC alignment and TLS.
- Keep a complete, accessible fallback message.
- Test with raw headers and controlled recipient accounts.
- Separate acceptance, placement, presentation and action metrics.
- Name every numerator, denominator and observation window.
- Monitor complaints, opt-outs and downstream outcomes.
- Set rollout ownership and rollback thresholds.
- Revalidate the current provider requirement before deployment.
Primary and contemporaneous references
- Google Workspace Updates: Expanding Gmail BIMI security: Primary evidence used to verify the dated event or current operating requirement.
- Google Admin Help: Set up BIMI: Primary evidence used to verify the dated event or current operating requirement.
- Google Workspace Updates: BIMI Common Mark Certificates: Primary evidence used to verify the dated event or current operating requirement.


